Executive summary
- Overnight on Monday, November 2, grocers, butchers, and small shops across Belgium, Estonia, Ireland, Luxembourg, The Netherlands, and Sweden reported cyber attacks on store refrigeration units.
- Attackers remotely raised store refrigeration unit temperatures to 50 degrees Celsius (122 degrees Fahrenheit), resulting in spoiled or melted food in dozens of stores.
- Reports suggest Danfoss StoreView refrigeration controllers, the product involved in October 11 attacks on French grocers, is also involved in this wave of attacks.
- Censys observes just over 1,000 Danfoss StoreView instances exposed globally, with the highest concentration in France.
- However, the 220 total exposures of Danfoss StoreView in France is down from 1,825 on October 11 prior to the attacks there. Of the 220 still online, 41% appear to be running a patched firmware version.
- 68% of StoreView instances in Belgium and 58% in Sweden appear to be running a patched version.
Introduction
In the early hours of Monday, November 2, stores in at least seven major supermarket chains, butchers, and small grocers across Europe suffered cyber attacks targeting their commercial refrigeration controllers, mirroring similar incidents observed in France three weeks ago.
This time, grocers in Belgium, Estonia, Ireland, Luxembourg, The Netherlands, and Sweden have reported attacks, and chains Carrefour, Coop, Delhaize, ICA, Selver, SuperValu, and Spar are among those impacted.
The attacks resemble those in France in both timing, targeting, and execution—early morning temperature adjustments meant employees were least likely to be able to immediately respond, and refrigerator temperatures in some stores were reportedly raised to 50 degrees Celsius (122 degrees Fahrenheit). Moreover, there are reports that the same Danfoss refrigeration controllers impacted in France several weeks ago were impacted in this wave of attacks.
Though the attacks are strikingly similar, no group has claimed responsibility, and it’s unconfirmed whether these were the work of the same actor.
The Censys ARC view
Below we examine global exposures of Danfoss StoreView refrigeration controllers. In August, Claroty Team82 researchers published findings on vulnerabilities in Danfoss products.
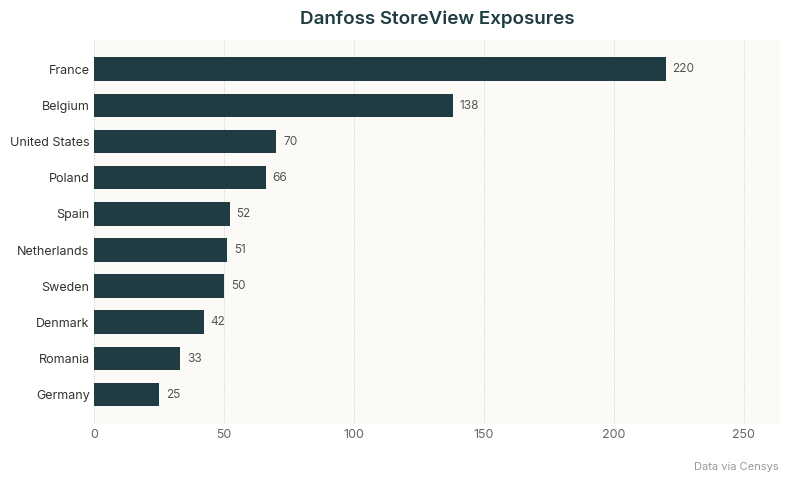
Top 10 countries with exposed Danfoss StoreView interfaces
France continues to lead Danfoss StoreView exposures globally, followed by Belgium and the U.S. Other European nations round out the top ten countries where exposures are observed.
As in our previous analysis, we used each StoreView host’s Last-Modified HTTP header to match the timestamp to the build date of the firmware. We note that France continues to show dramatic declines in StoreView exposures; prior to the attack in October, we observed 1,825 total exposures—regardless of firmware version—in France, with a steep decline over the subsequent days, landing at 537 on October 14. At the time of analysis, we observe only 220 total exposures of StoreView in France, 41% of which appear to be running a patched firmware version.
| Country | Total Hosts | Pre-4.2 | 4.2.4 | 4.3.1+ patched |
| France | 220 | 45% | 13% | 41% |
| Belgium | 138 | 28% | 4% | 68% |
| The Netherlands | 51 | 41% | 22% | 37% |
| Sweden | 50 | 38% | 4% | 58% |
Belgium leads in patching at 68% of total Danfoss StoreView instances running 4.3.1+, while Sweden is not far behind with 58% of instances on 4.3.1+.
We currently observe a small number of StoreView instances in Luxembourg (6, 4 of which are on 4.3.1+), Ireland (3, 2 of which are 4.3.1+), and Estonia (2, both patched).
Conclusion
Recent attacks on commercial refrigeration controllers serve as a reminder of the dangers these Internet-connected systems can pose to daily life and business operations. This is an evolving situation and Censys ARC will continue to assess the exposure and remediation of these systems.