Do you want ants? Because this is how you get ants.
Executive Summary
- Attackers targeted refrigeration units at hundreds of supermarkets across France over the weekend of October 10, resulting in spoiled food and, in some cases, fires.
- The attacks affected the Internet-exposed management interfaces of Danfoss refrigeration controllers. While Danfoss has not confirmed the exact initial access vector, it says most affected controllers were either older models that no longer received security updates or newer models running outdated firmware.
- Danfoss patched several vulnerabilities in its AK-SM 800A controllers more than a year earlier:
- CVE-2025-41450, disclosed in March 2025, allowed an unauthenticated actor to log in as an administrator using a code that could be computed from the current calendar date, without needing the admin password.
- CVE-2025-41451 and CVE-2025-41452, disclosed in August 2025, could allow authenticated users to run commands and disrupt the controller’s management interface.
- In August 2026, researchers at Claroty demonstrated how CVE-2025-41450 and CVE-2025-41451 could be chained together to achieve remote code execution.
- The incident prompted CERT-FR to issue an emergency alert and call for immediate removal of these controllers from the Internet.
- The larger security issue here is the continued Internet exposure of operational technology that is difficult or impossible to patch. End-of-life refrigeration controller models, much like other industrial equipment, can remain in service for years because replacing or repairing them is expensive. Over the long term, the oldest and least supported software tends to be what lingers longest on the Internet, a pattern we look at in more detail in our 2026 State of the Internet Report.
On the night of 11 October, attackers switched hundreds of French supermarket fridges into defrost mode. If that sounds familiar: in August, the Department of Defense confirmed refrigeration disruptions at US military commissaries, where at least one base reported that all its freezers had gone into defrost mode. The Department has not said what caused it or which equipment was involved.
While the August military commissaries hack has no confirmed vendor, the attacks on France do: Danfoss, specifically the Danfoss StoreView product.
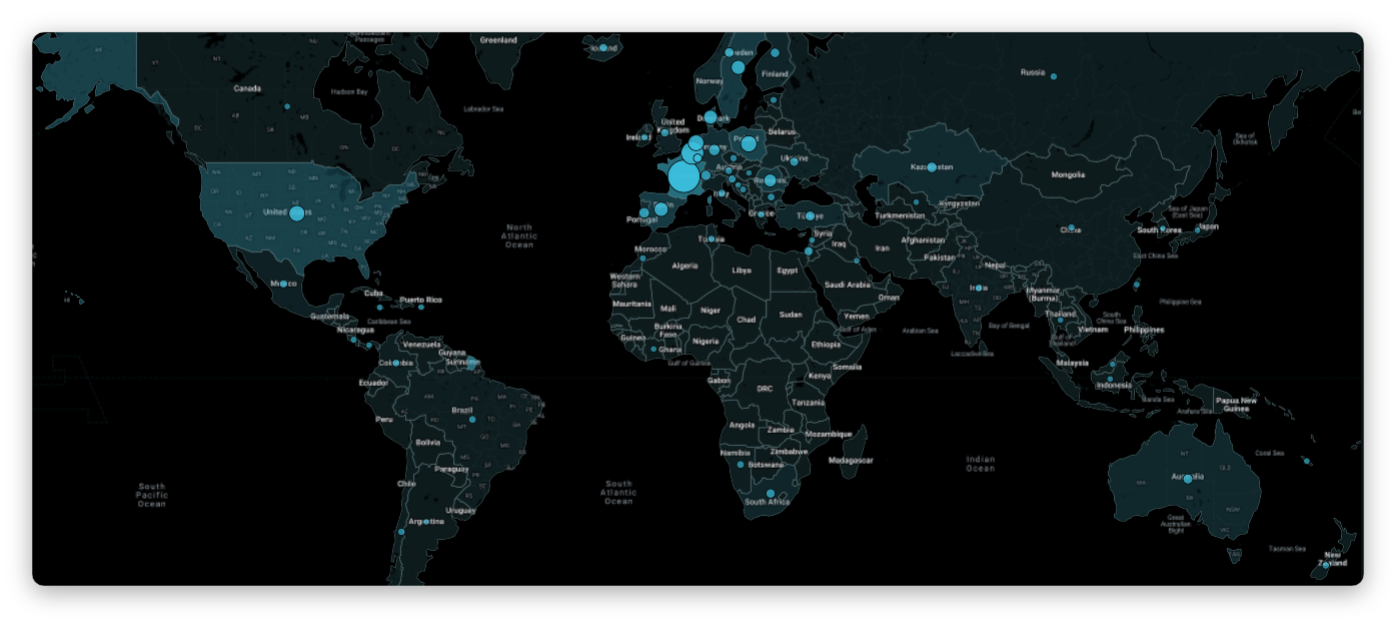
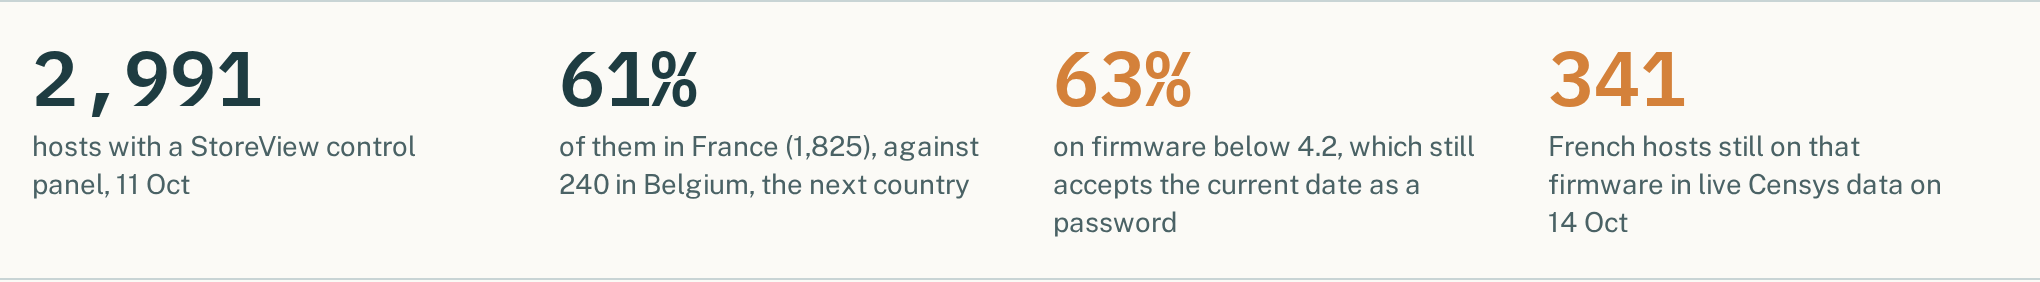
We reviewed every Danfoss StoreView control panel Censys found online and identified the version running on each host. Before the attack, 61% of these devices were in France, and most ran a version where the admin password could be derived from the current date.
France, Compared to the Rest of the World
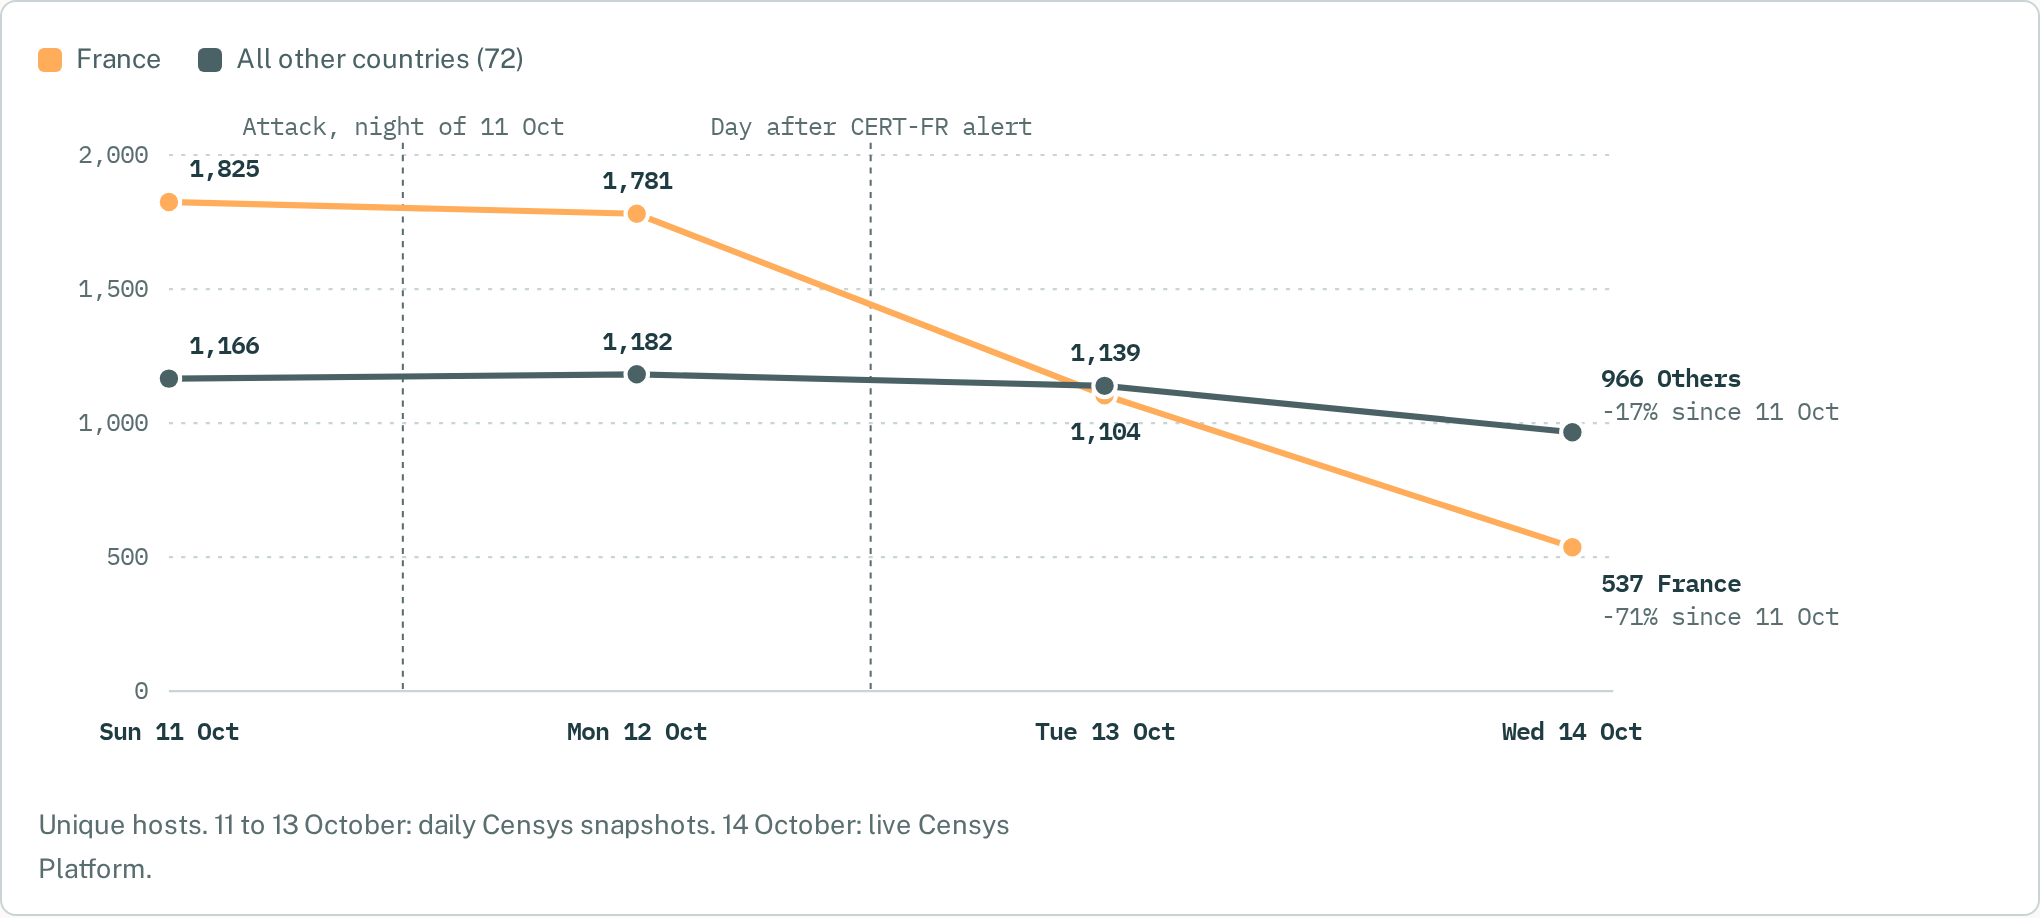
The number of StoreView control panels in France went from 1,825 hosts on October 11th to 1,781 on October 12th; in our latest numbers, it fell to 537 on October 14th, 2026.
Elsewhere, the change isn’t as dramatic: the number of hosts started at 1,166 and fell to 966 over the same time period.
This is expected, since most of the damage seems isolated to France or unreported elsewhere.
Below is a graph showing the dramatic decrease in the number of hosts running these Danfoss StoreView controllers in France, and a minimal decrease everywhere else.
In France, Patched and Unpatched Controllers Disappeared at the Same Rate
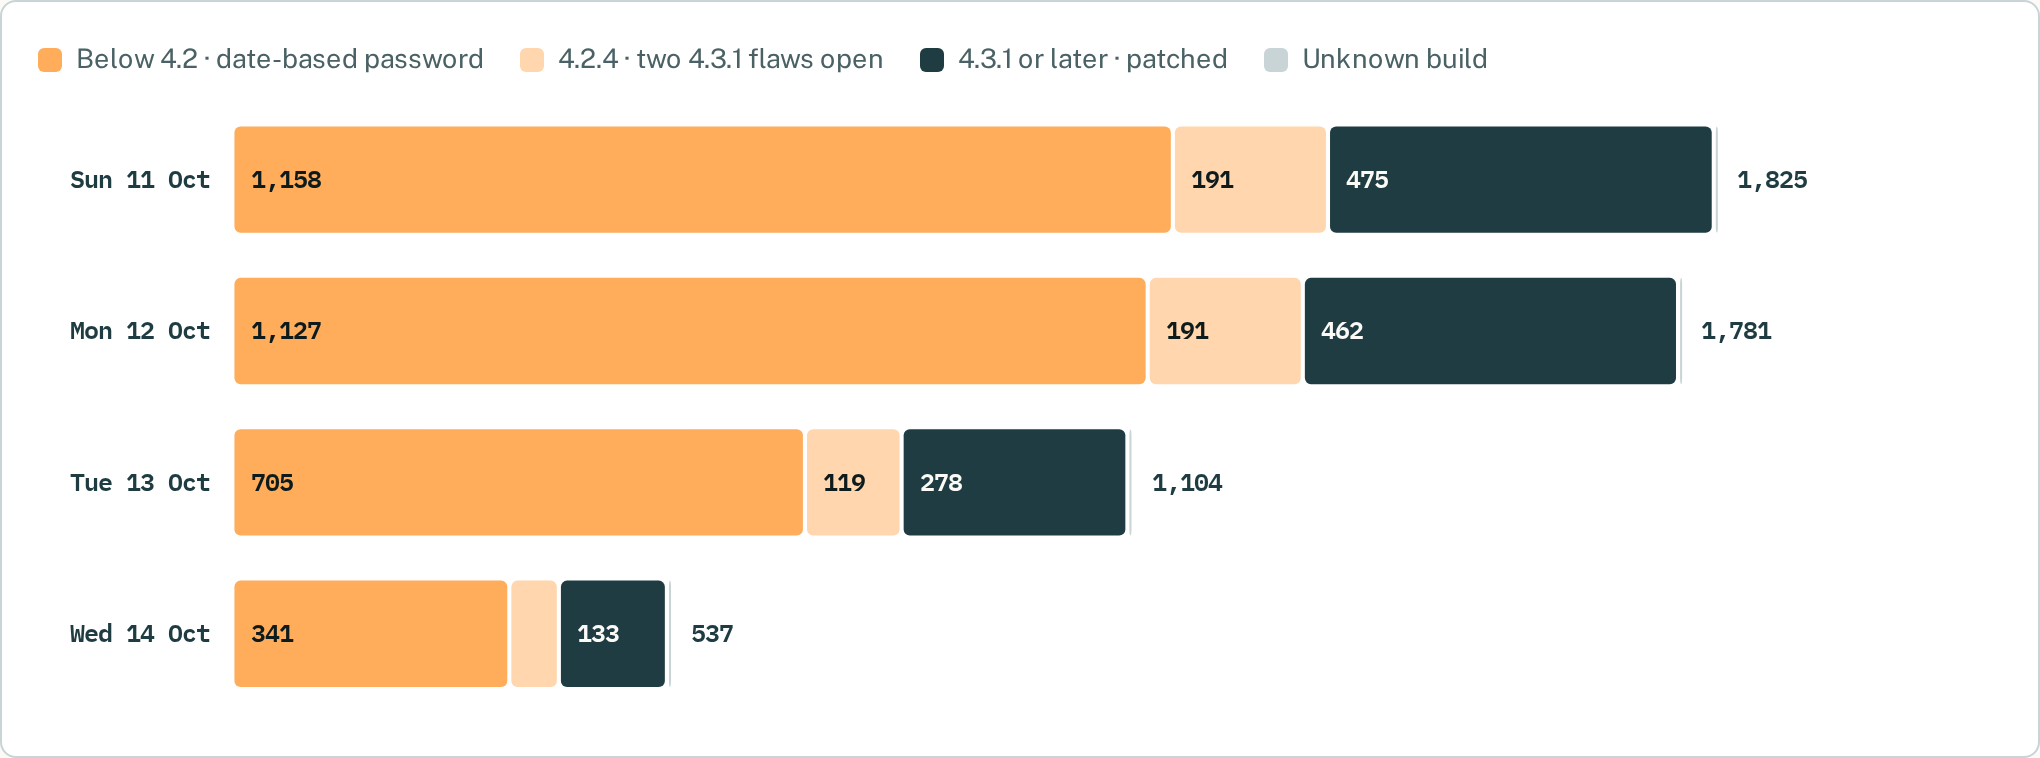
What’s interesting is that operators don’t appear to be patching their controllers; they’re simply taking them off the Internet. Patching would have left a mark in the data: the share on 4.3.1 or later (the releases that fix all three CVEs) would have grown in the table below. Instead, every group shrank by roughly the same amount, about 70%. Frankly, this is probably the best choice; there is no reason these should be directly connected to the Internet.
| France | 11 Oct | 12 Oct | 13 Oct | 14 Oct (live) | Change |
|---|---|---|---|---|---|
| Below 4.2 (date-based password) | 1,158 | 1,127 | 705 | 341 | -71% |
| 4.2.4 (two 4.3.1 flaws open) | 191 | 191 | 119 | 61 | -68% |
| 4.3.1 or later (patched) | 475 | 462 | 278 | 133 | -72% |
| Unknown build | 1 | 1 | 2 | 2 | +1 host |
| Total | 1,825 | 1,781 | 1,104 | 537 | -71% |
Worldwide, Most Controllers Run Firmware Older than 4.2 (Current is 5.3.2)
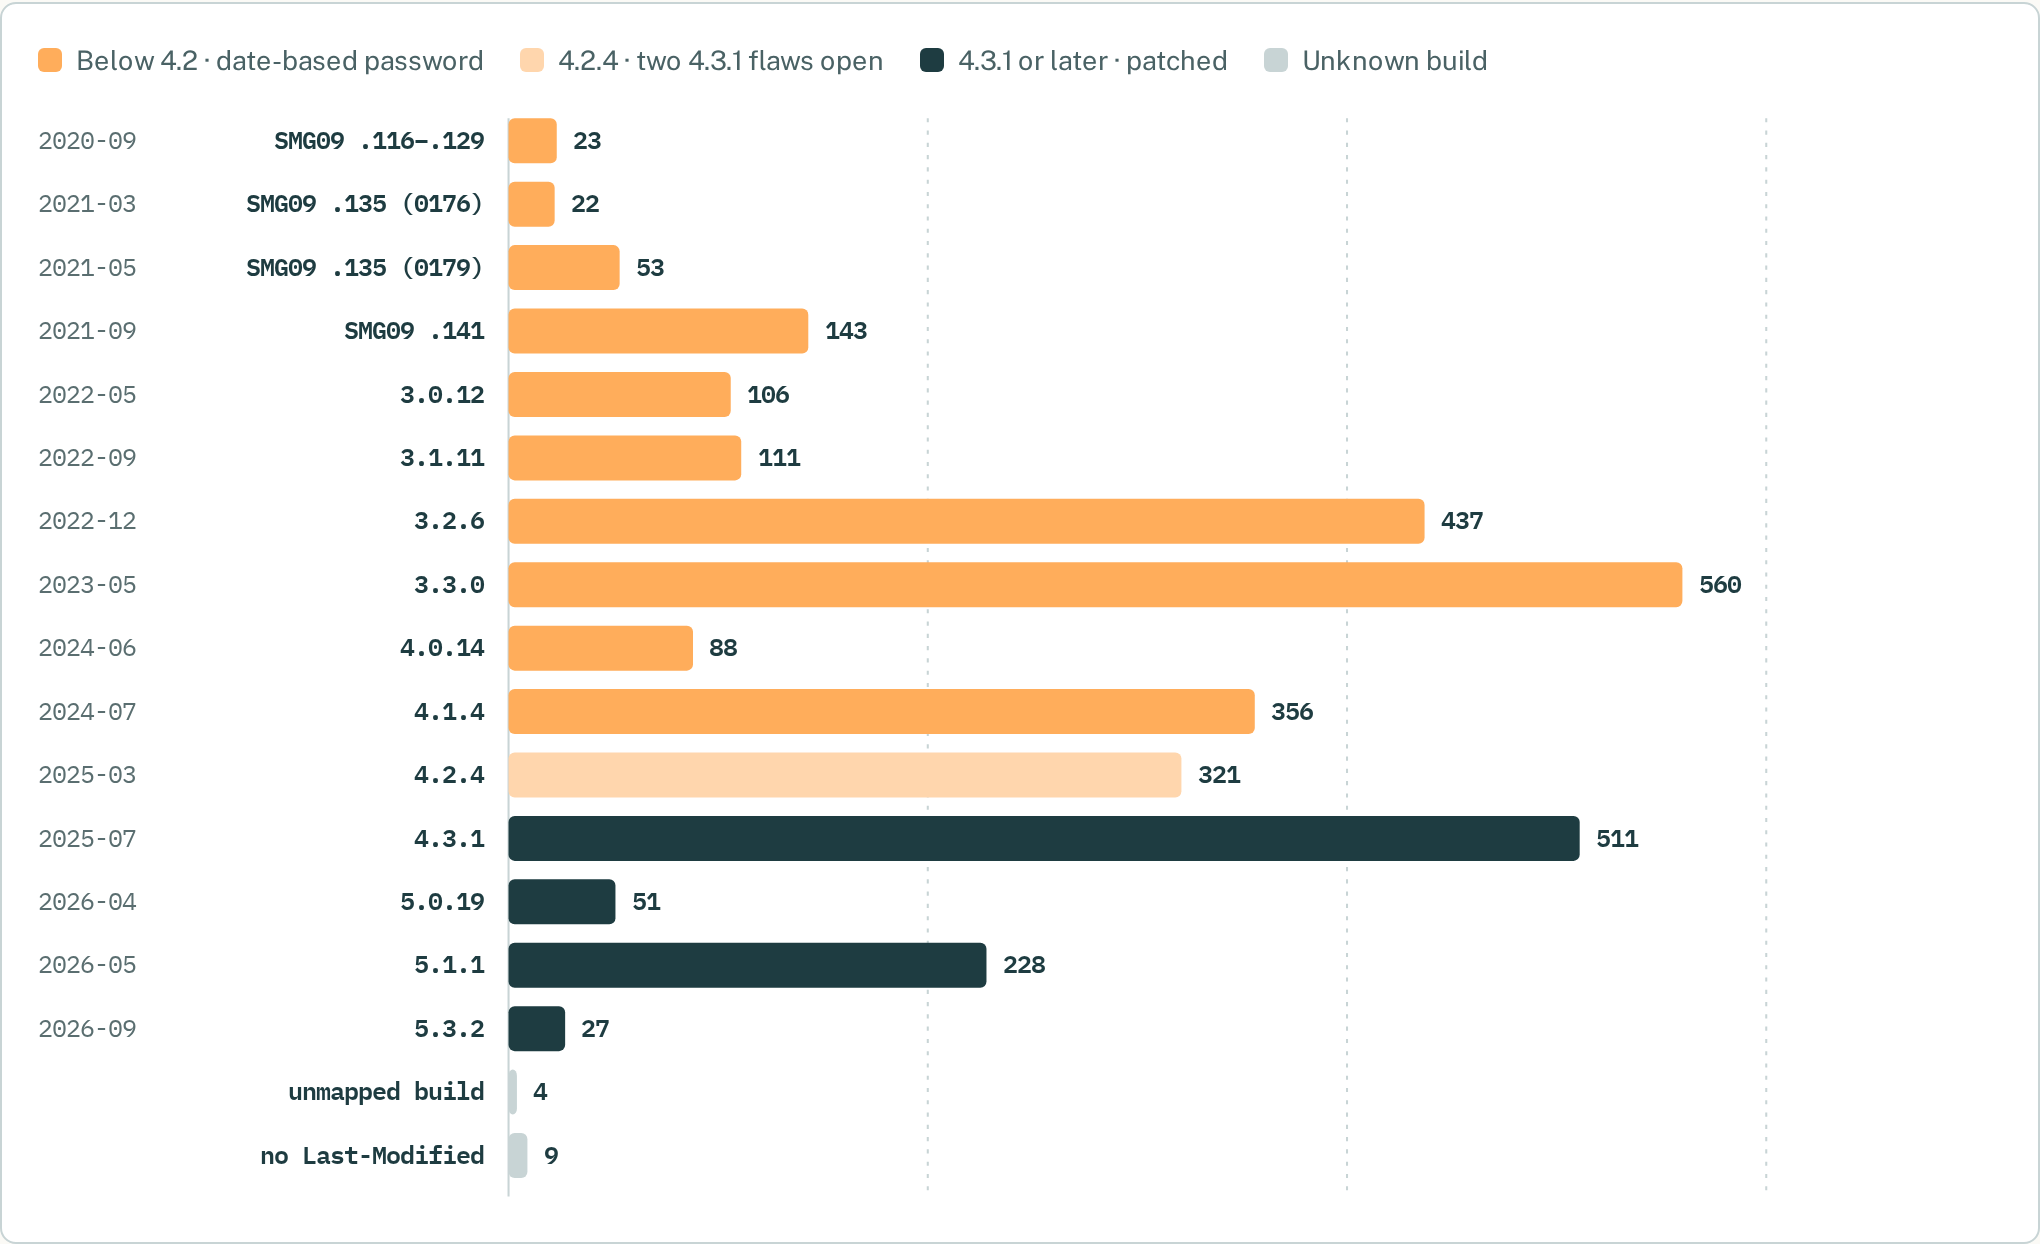
The chart below breaks down exposed controllers by firmware version on 11 October, the day of the attack, oldest build first. The three largest groups are 3.3.0 (built May 2023) with 560 hosts, 4.3.1 with 511, and 3.2.6 (December 2022) with 437.
| Firmware | Built | 11 Oct | 12 Oct | 13 Oct | 14 Oct (live) |
|---|---|---|---|---|---|
| SMG09 .116–.129 | 2020-09 | 23 | 22 | 13 | 5 |
| SMG09 .135 (0176) | 2021-03 | 22 | 22 | 11 | 7 |
| SMG09 .135 (0179) | 2021-05 | 53 | 53 | 43 | 34 |
| SMG09 .141 | 2021-09 | 143 | 137 | 111 | 69 |
| 3.0.12 | 2022-05 | 106 | 101 | 69 | 35 |
| 3.1.11 | 2022-09 | 111 | 113 | 91 | 52 |
| 3.2.6 | 2022-12 | 437 | 430 | 336 | 213 |
| 3.3.0 | 2023-05 | 560 | 554 | 414 | 285 |
| 4.0.14 | 2024-06 | 88 | 90 | 63 | 41 |
| 4.1.4 | 2024-07 | 356 | 358 | 257 | 150 |
| 4.2.4 | 2025-03 | 321 | 325 | 244 | 167 |
| 4.3.1 | 2025-07 | 511 | 502 | 363 | 228 |
| 5.0.19 | 2026-04 | 51 | 52 | 40 | 31 |
| 5.1.1 | 2026-05 | 228 | 223 | 180 | 132 |
| 5.3.2 | 2026-09 | 27 | 28 | 35 | 81 |
| unmapped build | n/a | 4 | 4 | 5 | n/a |
| no Last-Modified | n/a | 9 | 8 | 16 | n/a |
Old Firmware Isn’t a Problem Isolated to France
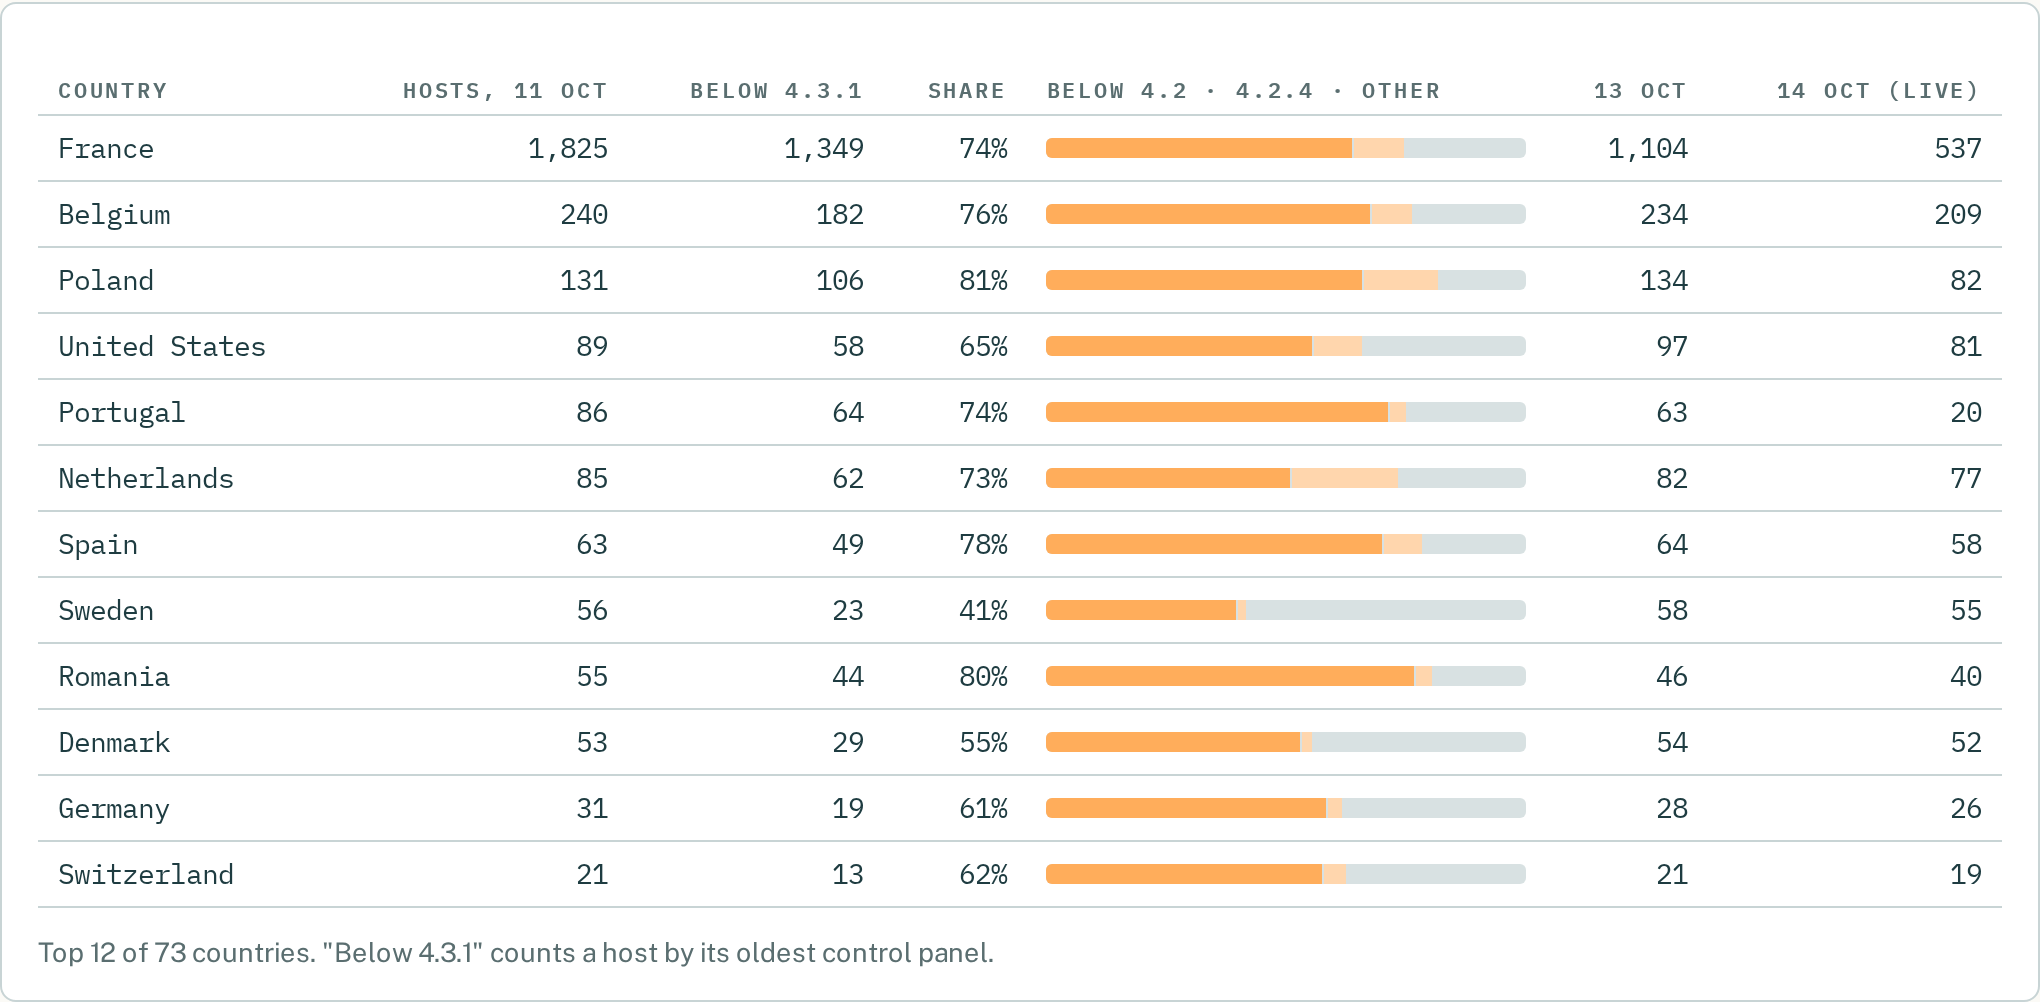
The chart below shows the 12 countries with the most exposed StoreView hosts on October 11th. The orange bars show the share of hosts on firmware below 4.3.1: darker orange is below 4.2 (vulnerable to all three published CVEs (CVE-2025-41450, CVE-2025-41451, CVE-2025-41452)), and lighter orange is version 4.2.4, which fixed the date-based login (CVE-2025-41450) but is still vulnerable to CVE-2025-41451 and CVE-2025-41452. The remaining gray is version 4.3.1 or later, which fixes all three CVEs.
Surprisingly, ten of the twelve countries have more than 60% of their hosts below version 4.3.1, led by Poland at 81% and Romania at 80%.
Version Extraction
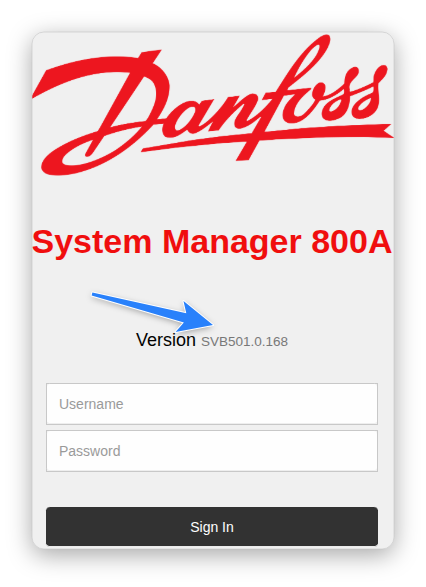
Unfortunately, the version number on the Danfoss devices’ login screen doesn’t match the version listed in the CVEs; the login-page version seems to be a “web interface” version, not the actual firmware version.
But, as it turns out, we can determine the versions using the Last-Modified HTTP header values, and we verified this with actual Danfoss updates.
We can grab the actual versions of this software dating back to 2020 using Danfoss’s public repository:
$ curl -s https://sm800a.danfoss.com/sw_shared/ | sort

SM800A_0135_SMG09.000.116_SVB501.000.120.spk

SM800A_0138_SMG09.000.116_SVB501.000.124.spk

SM800A_0140_SMG09.000.118_SVB501.000.124.spk

SM800A_0149_SMG09.000.129_SVB501.000.124.spk

SM800A_0176_SMG09.000.135_SVB501.000.139.spk

SM800A_0179_SMG09.000.135_SVB501.000.139.spk

SM800A_0187_SMG09.000.141_SVB501.000.141.spk

SM800A-3.0.12.spk

SM800A-3.1.11.spk

SM800A-3.2.6.spk

SM800A-3.3.0.spk

SM800A-4.0.14.spk

SM800A-4.1.4.spk

SM800A-4.2.4.spk

SM800A-4.3.1.spk

SM800A-5.0.19.spk

SM800A-5.1.1.spk

SM800A-5.3.2.spk
We downloaded all 18 of these files, and as an example, here is the 4.3.1 update, with its fingerprint so anyone can check if they have the same file:
$ curl -sO https://sm800a.danfoss.com/sw_shared/SM800A-4.3.1.spk

$ sha256sum SM800A-4.3.1.spk

5a19ee33d9d9fa26302bbf2b1875475c9e97979528fd382e87de39a645b96af2  SM800A-4.3.1.spk
Next, we look at the contents of the archive:
$ TZ=UTC 7z l SM800A-4.3.1.spk

...

2025-07-31 08:32:44 ....A          345     28487960  cert.ssl

2025-07-31 08:28:52 ....A           91               cert.txt

2025-07-31 08:30:46 ....A          827               cert.txt.asc

2025-07-31 08:27:53 ....A     28551406               SM800A_Upgrade_Source.7z
And then we need to extract the second archive embedded inside that one, SM800A_Upgrade_Source.7z, with the following:
$ 7z e SM800A-4.3.1.spk SM800A_Upgrade_Source.7z

...

Everything is Ok
And finally, we can look at the timestamp of the public html/index.html:
$ TZ=UTC 7z l SM800A_Upgrade_Source.7z html/index.html

...

2025-07-31 08:18:58 ....A          772               html/index.html
So now we know that the login page file in 4.3.1 was last changed at 2025-07-31 08:18:58 UTC. In other words, that’s when Danfoss packaged and built the 4.3.1 update.
We can then repeat this process for every single update we downloaded:
$ for f in SM800A*.spk; do

  7z e -y -so "$f" SM800A_Upgrade_Source.7z > inner.7z 2>/dev/null

  TZ=UTC 7z l inner.7z html/index.html html_svb5/index.html |

    awk -v pkg="$f" '$NF ~ /index\.html$/ { print $1, $2, pkg, $NF }'

done

rm -f inner.7z

2020-08-11 19:00:25 SM800A_0135_SMG09.000.116_SVB501.000.120.spk html/index.html

2020-09-03 18:39:16 SM800A_0138_SMG09.000.116_SVB501.000.124.spk html/index.html

2020-09-03 18:39:16 SM800A_0140_SMG09.000.118_SVB501.000.124.spk html/index.html

2020-09-03 18:39:16 SM800A_0149_SMG09.000.129_SVB501.000.124.spk html/index.html

2021-03-15 16:39:58 SM800A_0176_SMG09.000.135_SVB501.000.139.spk html/index.html

2021-05-05 13:18:46 SM800A_0179_SMG09.000.135_SVB501.000.139.spk html/index.html

2021-09-29 11:43:19 SM800A_0187_SMG09.000.141_SVB501.000.141.spk html/index.html

2022-05-04 08:11:59 SM800A-3.0.12.spk html/index.html

2022-09-07 10:21:34 SM800A-3.1.11.spk html/index.html

2022-12-14 12:36:59 SM800A-3.2.6.spk html/index.html

2023-05-19 13:40:11 SM800A-3.3.0.spk html/index.html

2024-06-06 17:38:01 SM800A-4.0.14.spk html/index.html

2024-07-26 07:15:22 SM800A-4.1.4.spk html/index.html

2025-03-04 11:55:41 SM800A-4.2.4.spk html/index.html

2025-07-31 08:18:58 SM800A-4.3.1.spk html/index.html

2026-04-07 09:55:04 SM800A-5.0.19.spk html/index.html

2026-04-07 15:55:13 SM800A-5.0.19.spk html_svb5/index.html

2026-05-29 12:51:03 SM800A-5.1.1.spk html/index.html

2026-05-29 15:45:52 SM800A-5.1.1.spk html_svb5/index.html

2026-09-18 11:59:19 SM800A-5.3.2.spk html/index.html

2026-09-24 06:23:34 SM800A-5.3.2.spk html_svb5/index.html
Once we have all the dates, we can format them to match the HTTP Last-Modified header value in Censys (which we will not show here).
Search Queries
Because of the sensitivity of this matter, we will not post direct links to search for either the vulnerable or patched versions of this service. Instead, we will post a simple search query already available on other platforms.
Note: The 5.x versions include two web interfaces. It seems that from 5.0 on, Danfoss made its new “StoreView Web” interface the default but kept the older interface in the package; operators can switch back in the controller’s settings. So, these two search queries look for either.
Sources
- CERT-FR alert CERTFR-2026-ALE-012
- Danfoss security advisories (CVE-2025-41450 fixed in 4.2; CVE-2025-41451 and -41452 fixed in 4.3.1)
- CISA ICSA-25-140-03
- Claroty Team82 research
- Kevin Beaumont on Mastodon
- BFMTV (in French)
- The Guardian