Vulnerability Description
N-able responded on November 9, 2026 to a public release of technical write-ups and proof-of-concept code for what Field Effect reports as 33 alleged vulnerabilities in N-able N-central, N-able’s remote monitoring and management (RMM) platform. As of November 9, 2026, no CVE identifiers, CVSS scores, or NVD entries exist for these issues. N-able’s incident notice states: “N-able is currently responding to a public disclosure and non-responsible communication of critical vulnerabilities in N-central found by an independent researcher.”
As of November 9, 2026, N-able has published no mechanism detail, affected versions, or fixed versions. Field Effect’s analysis of the released material lists the claimed impacts as remote code execution, privilege escalation, administrator account creation, credential disclosure, configuration changes, account enumeration, audit record manipulation, remote-control session disruption, and device impersonation, and reports that the material alleges a mix of authenticated and unauthenticated vulnerabilities. Field Effect reads one proof-of-concept as an unauthenticated XML External Entity (XXE) flaw that can be chained into remote code execution. That reading is Field Effect’s. N-able’s notice does not confirm the count, the specific impacts, or the XXE chain, and no source has validated the proof-of-concept code.
Impact
Field Effect reads one public proof-of-concept file as an unauthenticated XXE flaw chained into remote code execution, and reports that the published material alleges administrator account creation among other outcomes. None of it has been validated. N-central is the control plane for the endpoints and networks an organization or managed service provider administers, so a compromised server puts at risk the credentials, scripts, and remote-control sessions it holds and every device it manages. N-able has taken its hosted environments offline and strongly advises on-premises customers to take their servers offline until further notice. Field Effect advises that where unauthorized activity is found, N-central administrator, service, and integration credentials be rotated, and that authentication activity, administrator account creation, privilege changes, script execution, remote-control sessions, and policy changes be reviewed, especially in the period before systems went offline.
Details
| CVE | None assigned yet |
| Date of Disclosure | November 8, 2026 |
| Affected Assets | N-able N-central, hosted and on-premises, in all three N-able regions (Americas, APAC, Europe), per N-able’s incident notice |
| Vulnerable Software Versions | None published by N-able; the independent researcher who released the PoC says pre-release build 2026.4.0.31 was tested and earlier builds are also affected |
| PoC Available | Yes, released publicly on November 9, 2026 by an independent researcher; the source is not an established security vendor, so it is not linked here |
| Exploitation Status | N-able states it had seen no active exploitation as of its November 9, 2026 notice |
| Patch Status | None yet; N-able states a hotfix is in development and expected soon, and hosted environments are offline pending remediation |
Censys Queries
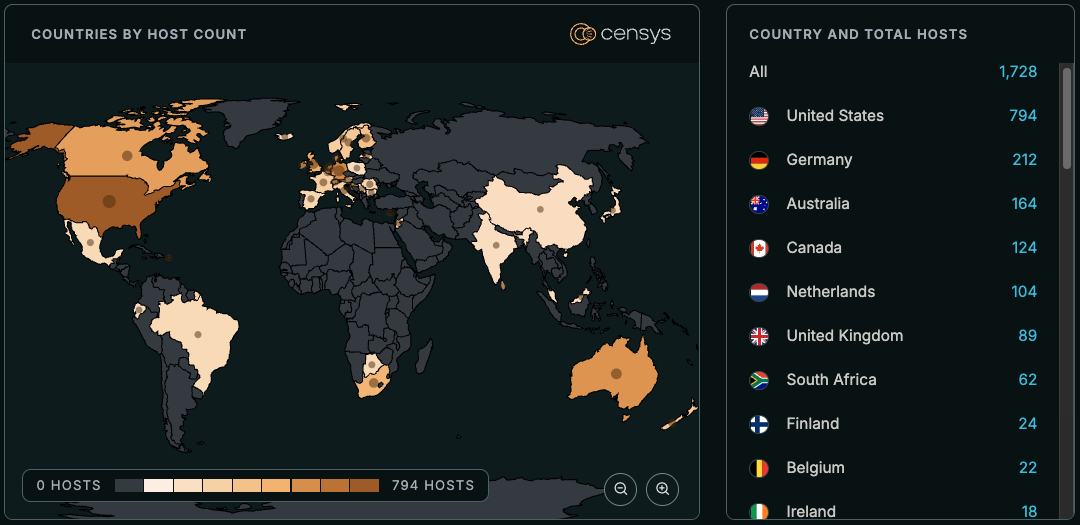
Platform: Found: 1,728 hosts
host.services.software:(vendor="n-able" and product="n-central") and host.services.endpoints.http.html_title:"N-central"
ASM:
host.services.software:(vendor="N-able" and product="N-central") or web_entity.instances.software:(vendor="N-able" and product="N-central")