Vulnerability Description
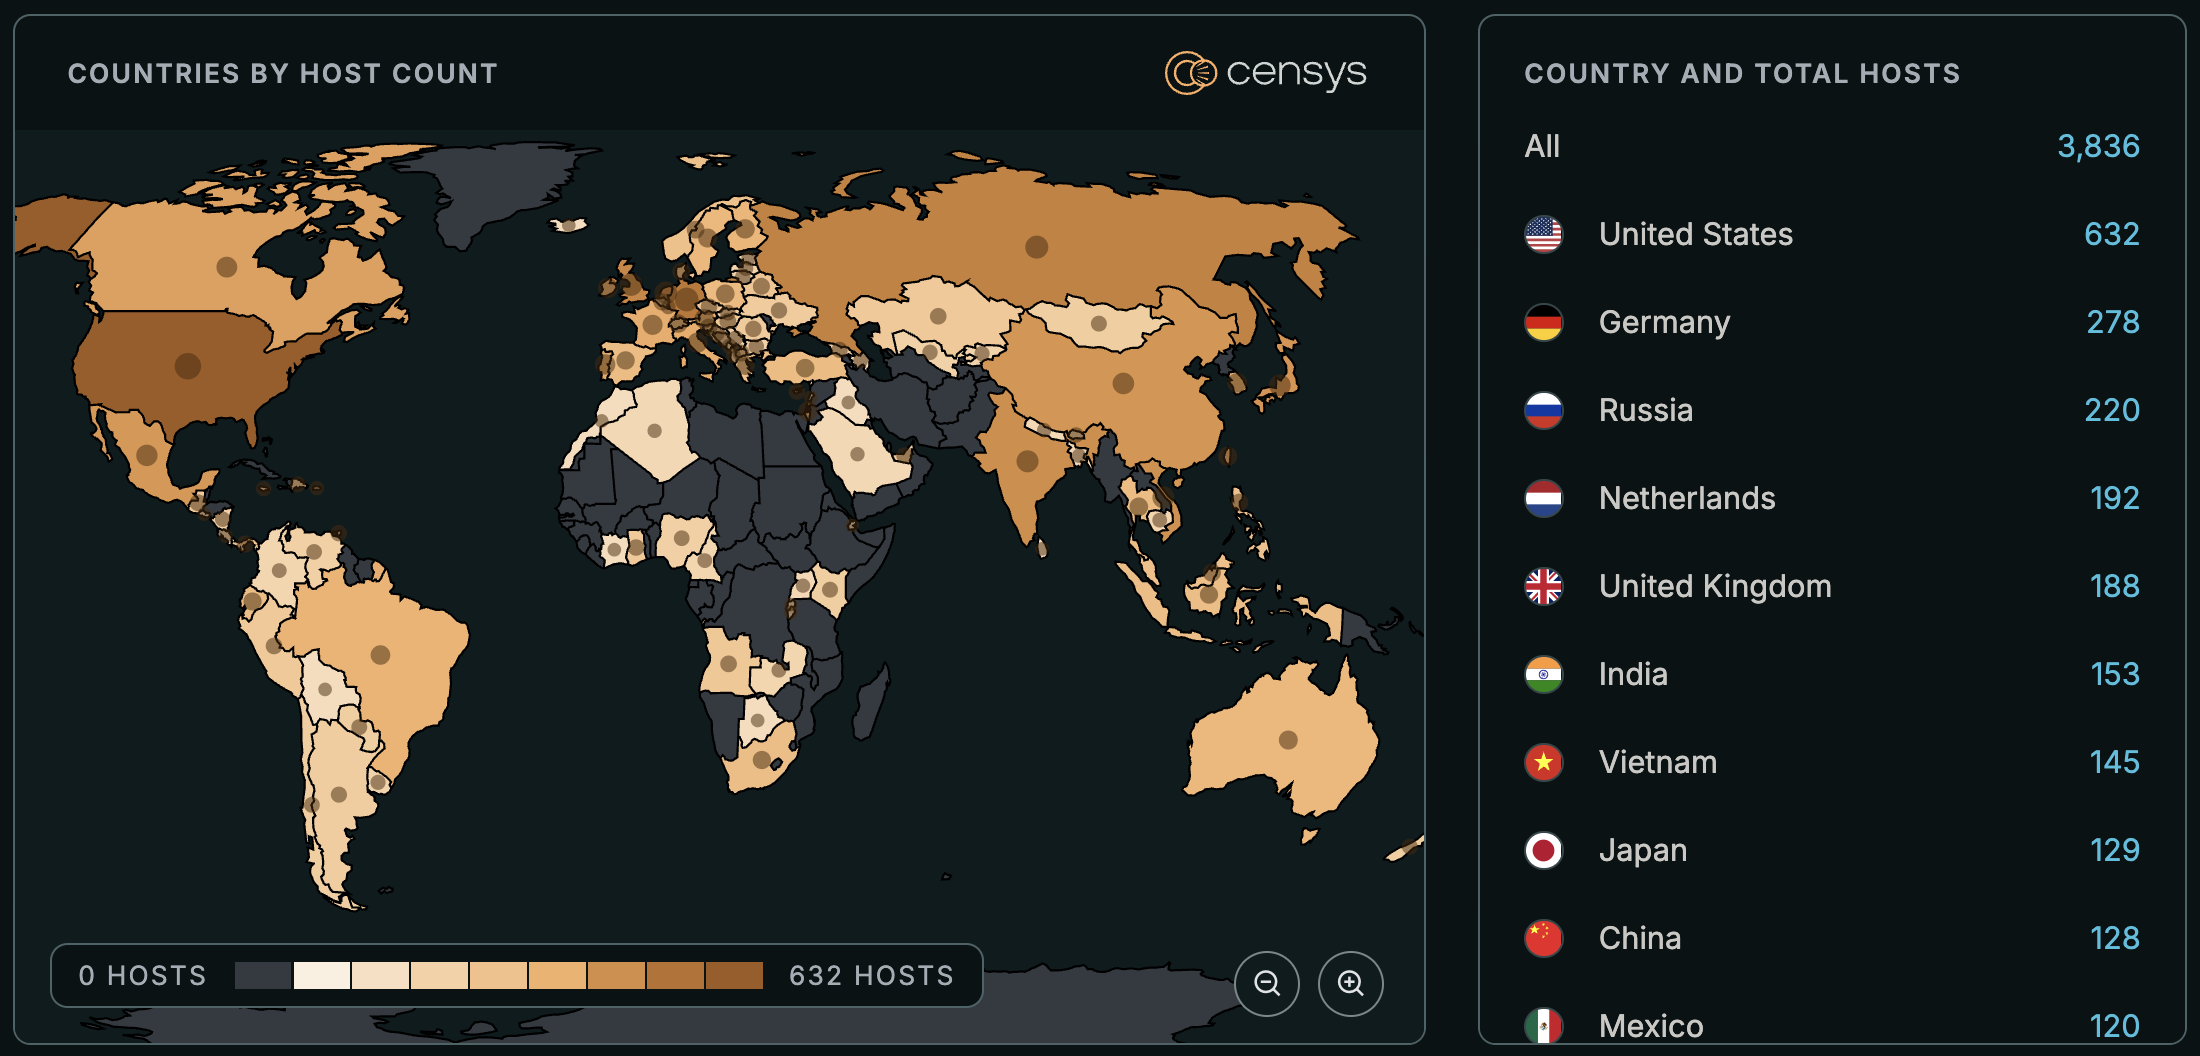
CVE-2026-91843 is a stack-based buffer overflow in the unauthenticated login process of Check Point Quantum Security Management Server and Log Server, including Multi-Domain variants, that allows a remote unauthenticated attacker to execute arbitrary code as root by sending a crafted login request with an excessively long username. Censys observes 3,836 hosts globally carrying the Security Management/Log Server role, identified by the Security Internal Communication (SIC) identity Check Point assigns management servers by default rather than by version, since build and Jumbo Hotfix level are not visible in passive scan data. This figure is total role presence, not a confirmed-vulnerable count.
Details
| Field | Description |
| CVE-ID | CVE-2026-91843, CVSS v3.1 9.8 (critical), assigned by Check Point. |
| Date of Disclosure | September 16, 2026. |
| Affected Assets | Self-managed Check Point Quantum Security Management Server and Log Server, including Multi-Domain variants. Smart-1 Cloud is not affected and requires no action. |
| Vulnerable Software Versions | R82.20 up to the latest build, R82.10 through Jumbo Hotfix Take 44, R82 through Take 126, R81.20 through Take 166, and R81.10, R81, and R80.x (all End of Support). |
| PoC Available | No, as of this writing. |
| Exploitation Status | Not confirmed. Not listed in CISA’s Known Exploited Vulnerabilities (KEV) catalog or VulnCheck’s KEV as of this writing. |
| Patch Status | Check Point has published patches for all affected branches. Fixed by R82.20 Take 29, R82.10 Take 28, R82 Take 28, and R81.20 Take 28, distributed via LivePatch. |
Affected Assets
Per Check Point sk1000155, the following versions are affected unless the listed Jumbo Hotfix Take (or higher) is installed:
- R82.20: all versions (no Jumbo Hotfix currently provides protection)
- R82.10: Jumbo Hotfix Take 44 or below
- R82: Jumbo Hotfix Take 126 or below
- R81.20: Jumbo Hotfix Take 166 or below
- R81.10 (End of Support): Jumbo Hotfix Take 190 or below
- R81, R80.40, R80.30, R80.20, R80.10, R80 (all End of Support): all versions
Smart-1 Cloud, Check Point’s SaaS-hosted management offering, is explicitly not affected; Check Point deployed the fix there ahead of public disclosure. The advisory does not distinguish a separate release cadence for Multi-Domain deployments; the same version and Take numbers apply to both.
Censys observes 3,836 hosts (Platform) exposing the cp_mgmt SIC identity that Check Point assigns to Security Management and Log Servers by default. This figure counts total product and role presence, not confirmed-vulnerable or version-filtered hosts.
Censys Query
Platform: Found: 3,836 hosts (view on Platform)
host.services.checkpoint_topology.common_name: "cp_mgmt"
This query identifies the Check Point Security Management/Log Server role by its Security Internal Communication (SIC) identity rather than by version, so it matches product and role presence, not a specific patch level. A port-based signal (CPMI, port 18190) was considered but excluded: live testing found unrelated services, including a cPanel host, answering on that same port, so it isn’t Check Point specific.
PoC Available?
No public proof-of-concept exists as of this writing.
Exploitation Status
Not confirmed. CVE-2026-91843 does not appear in the CISA Known Exploited Vulnerabilities (KEV) catalog or in VulnCheck’s KEV, and no sensor reporting or national CERT advisory has described in-the-wild exploitation as of this writing. Don’t read that as safe, though: a pre-auth RCE against network security management infrastructure tends to get weaponized fast once someone publishes a working trigger.
Patch Status
Check Point distributes the fix via LivePatch, not a standalone build. Patched Jumbo Hotfix Takes are R82.20 Take 29, R82.10 Take 28, R82 Take 28, and R81.20 Take 28. Systems with automatic updates enabled per sk175504 receive the fix automatically. R81.10, R81, and the R80.x branches are End of Support and get no fix at all; upgrading to a supported branch is the only way to remediate.
References
- Check Point sk1000155 (vendor advisory: description, affected versions, Jumbo Hotfix Take numbers, LivePatch remediation)
- Check Point sk175504 (automatic update enrollment, referenced by the vendor advisory as the path to automatic protection)
- NVD: CVE-2026-91843 (CVSS scoring, CWE-121 classification)
- CVE.org record (CNA record, Check Point Software Technologies Ltd.)