Vulnerability Description
CVE-2026-90436 is an unauthenticated remote code execution flaw in the Apache Axis 1.x library (CVSS v3.1 9.8, scored by CISA’s ADP; Atlassian rates it CVSS v4.0 9.3). It affects Atlassian Confluence Data Center because Confluence uses Axis for its XML-RPC and SOAP APIs. According to the Apache Software Foundation, “Deserialization of an inbound SOAP fault in Apache Axis 1.x allows unauthenticated remote class instantiation. When a SOAP <Fault> carries a <detail><exceptionName> element, Axis loads the named class and, if a String <data> element is also present, instantiates it through its String constructor before checking that it is an AxisFault. Loading alone runs the class’s static initializer. With a suitable class on the application’s classpath this leads to remote code execution. The fault is parsed while the engine resolves the target service, before any per-service handler chain runs, so authentication handlers configured on a service do not protect against it.”
Atlassian’s advisory lists Confluence Data Center 1.x.x through 9.x.x as affected and says exploitation requires the Remote API (XML-RPC & SOAP) setting to be enabled. Atlassian says that setting has been off by default for new installations since Confluence 3.0, and it removed the feature in Confluence 10.0, which is why 10.x is not affected.
The same Axis flaw is the initial-access step in the 4EverAble2Shell chain against N-able N-central, where BleepingComputer reports that exploitation also depends on a non-default setting, the Legacy API. Apache lists no downstream products and does not expect to release a fixed Axis 1.x version, so each vendor that bundles Axis 1.x has to publish its own assessment. Atlassian has published one, and the Debian security tracker lists Debian’s axis package as vulnerable with no fix.
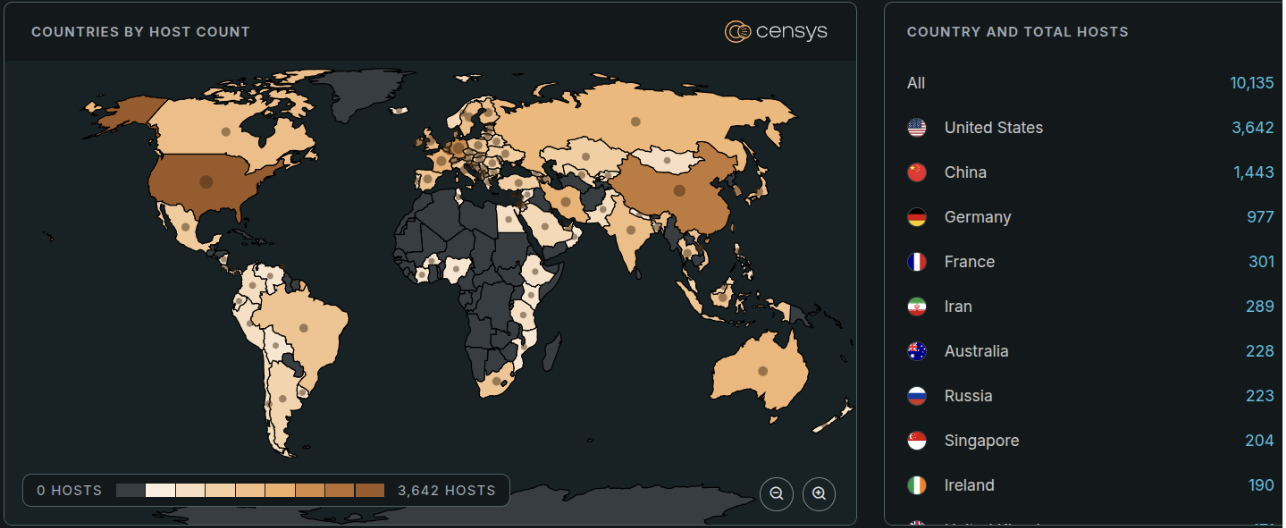
Hosts running Atlassian Confluence, from a Platform host search. A host is one IP address, so this count is lower than the web property figure below, which counts every hostname and port.
Impact
The public proof-of-concept for the underlying Axis flaw instantiates a JDK class that creates or truncates files in a lab service, and the N-central chain uses the same flaw to run commands as the nable service account before escalating to root. Rapid7 detected exploitation against Confluence Data Center in a customer environment, first observed November 13, 2026, and has not described what the attacker did afterward, so the demonstrated impact on Confluence is what Atlassian states: remote code execution. Confluence instances with the Remote API enabled should be upgraded to 9.2.28 or the latest release now. Where that must wait, disabling the Remote API setting is Atlassian’s interim mitigation, which limits reach without fixing the flaw. Atlassian says it cannot confirm whether a customer’s instances have been affected and advises checking them for evidence of compromise. Rapid7 publishes the IP addresses associated with the Confluence activity.
Details
| CVE | CVE-2026-90436, critical, CVSS v3.1 9.8 (CISA ADP) and CVSS v4.0 9.3 (Atlassian), assigned by the Apache Software Foundation |
| Date of Disclosure | November 6, 2026 |
| Affected Assets | Confluence Data Center with the Remote API (XML-RPC & SOAP) setting enabled; Atlassian Cloud sites are not affected, and Atlassian’s advisory does not address Confluence Server |
| Vulnerable Software Versions | Confluence Data Center 1.x.x through 9.x.x; 10.0 and later are not affected |
| PoC Available | Yes for the underlying Axis flaw: a public lab proof-of-concept first published November 10, 2026 creates or truncates files and does not demonstrate code execution against Confluence; a separate public exploit chain for N-able N-central was published November 12, 2026 |
| Exploitation Status | Exploited against Confluence Data Center (Rapid7 MDR, first observed November 13, 2026) and against N-able N-central (Huntback reports at least 21 compromised production servers, per BleepingComputer) |
| Patch Status | Fixed in Confluence Data Center 9.2.28, the only fixed build Atlassian names; Atlassian recommends the latest release or a fixed LTS release and offers disabling the Remote API setting as a mitigation; Apache does not expect to release a fixed Axis 1.x version but published a patch commit |
Censys Queries
Platform: Found: 1,212,568 web properties
web.software: (vendor="atlassian" and product="confluence_server") and not web.labels.value: "HONEYPOT"
A match shows Confluence is present and says nothing about the version or the Remote API setting.
ASM:
(host.services.software:(vendor={"Atlassian","atlassian"} and product={"Confluence","Confluence Server","confluence","confluence_server","Confluence Data Center"}) and not host.services.labels: {honeypot, tarpit}) or web_entity.instances.software:(vendor={"Atlassian","atlassian"} and product={"Confluence","Confluence Server","confluence","confluence_server","Confluence Data Center"})
References
- Atlassian security advisory for CVE-2026-90436
- NVD entry for CVE-2026-90436
- Apache Axis security announcement
- Rapid7: Exploitation of CVE-2026-90436 against Confluence Data Center and N-able N-central
- BleepingComputer: N-able 4EverAble2Shell zero-day exploited hours after PoC released
- Debian security tracker for CVE-2026-90436