Vulnerability Description
CVE-2026-85706 is a path traversal vulnerability in self-managed GitLab Community Edition and Enterprise Edition, scored CVSS v3.1 10.0 by GitLab as the CNA. GitLab attributes it to improper path confinement and missing authentication enforcement in the repository commits API, which lets an unauthenticated remote attacker read arbitrary files from the server. It is listed in the CISA Known Exploited Vulnerabilities (KEV) catalog and is under active exploitation in the wild.
Impact
Public exploit code demonstrates reading /etc/gitlab/gitlab-secrets.json, which holds the keys GitLab uses to encrypt secrets it stores such as CI/CD variables, deploy keys, and integration tokens. Those are the credentials the instance’s pipelines use to reach everything else, so the exposure extends to the cloud accounts, container registries, and repositories they authenticate to. If your instance was reachable from the internet while unpatched, treat these credentials as compromised. Rotate them and review the instance for signs of use.
Details
| Field | Description |
| CVE-ID | CVE-2026-85706, CVSS v3.1 10.0 (critical), assigned by GitLab. |
| Date of Disclosure | GitLab: September 10, 2026. NVD: September 12, 2026. |
| Affected Assets | Self-managed GitLab Community Edition and Enterprise Edition. GitLab.com and GitLab Dedicated are not affected and require no action. |
| Vulnerable Software Versions | 18.7 through 19.1.7, 19.2.0 through 19.2.5, and 19.3.0 through 19.3.1. |
| PoC Available | Yes, first published September 12, 2026, with 12 or more public exploit repositories by September 14. |
| Exploitation Status | Added to CISA’s Known Exploited Vulnerabilities (KEV) catalog on September 11, 2026, confirming active exploitation, with a remediation due date of September 14, 2026. |
| Patch Status | GitLab has published patches for all affected branches. Fixed by 19.3.2, 19.2.6, and 19.1.8, released September 10, 2026. |
Censys Queries
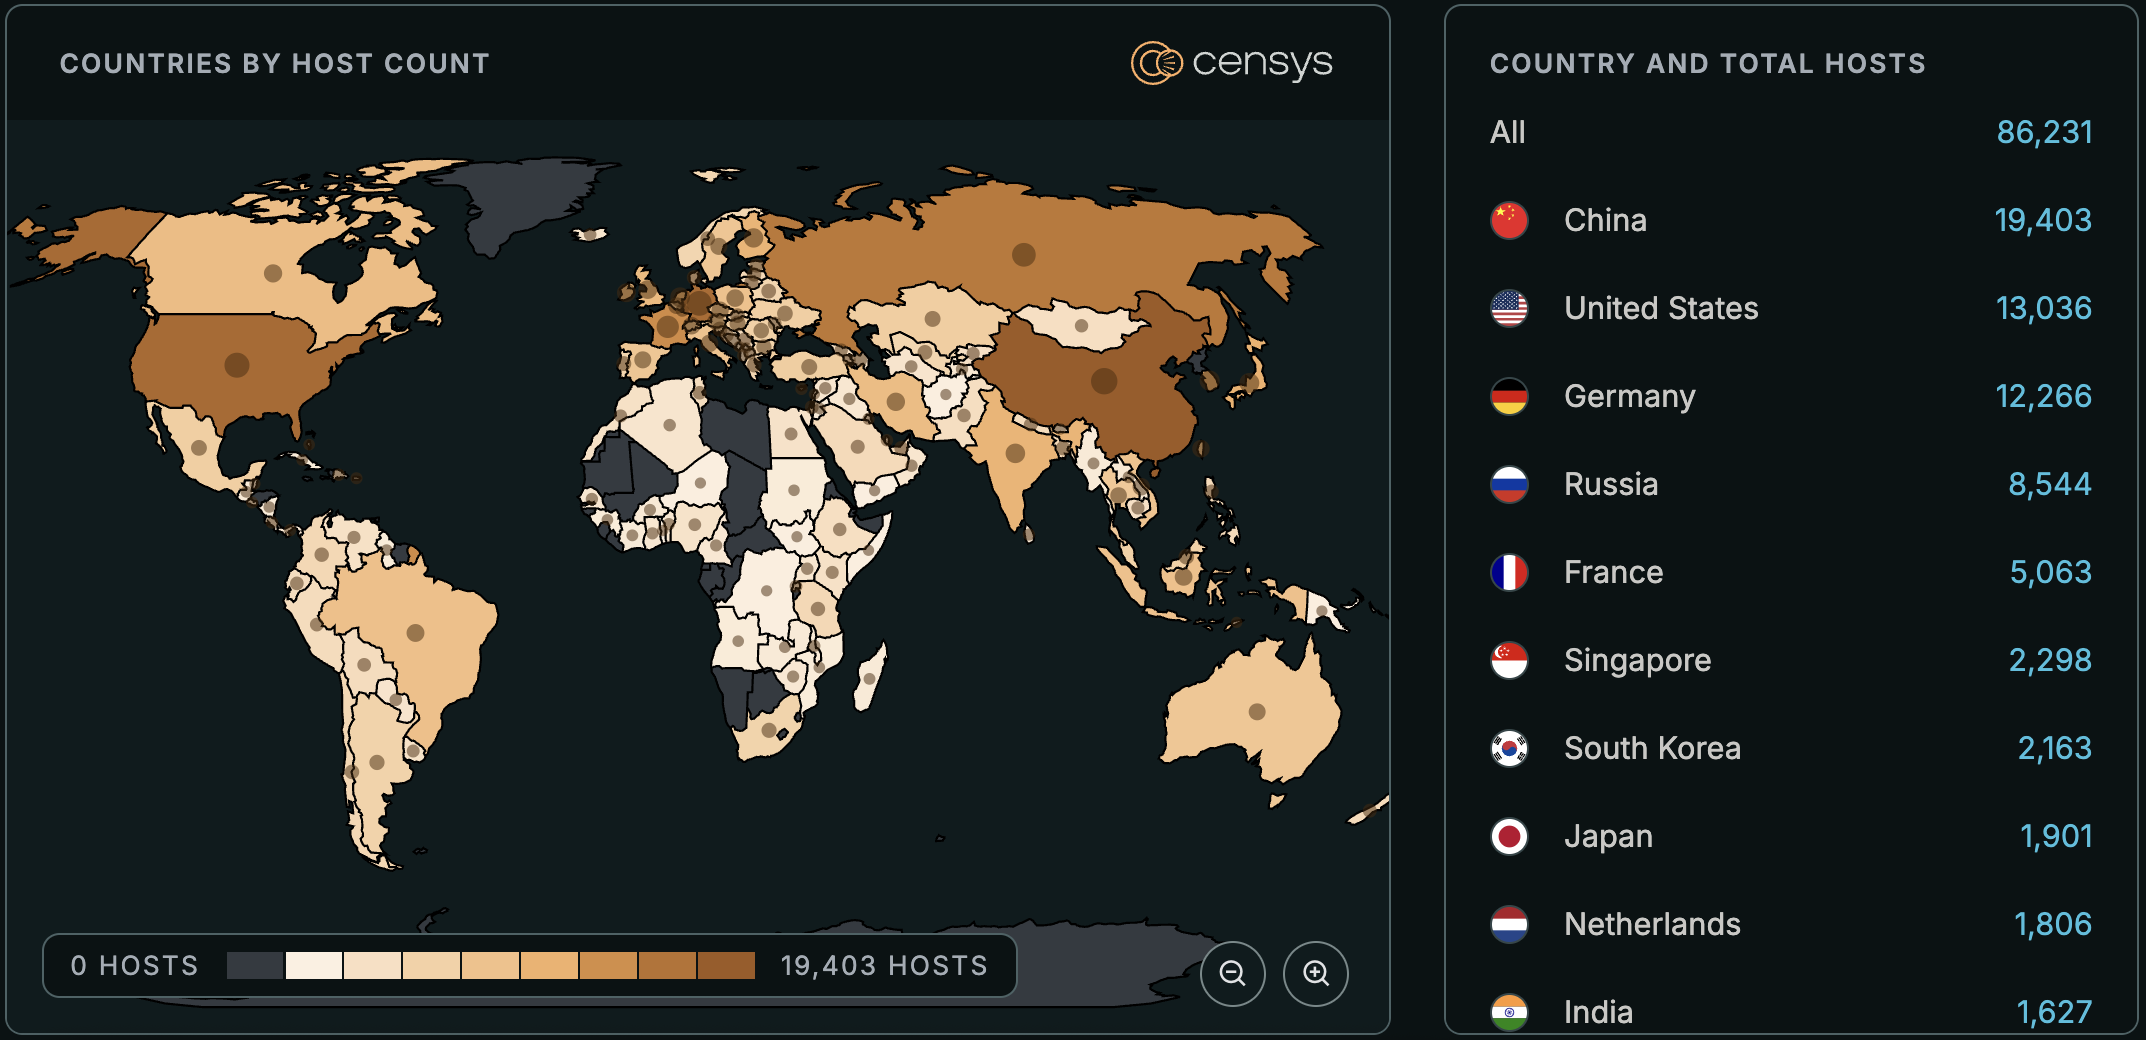
Platform: Found 86,062 hosts and 208,186 web properties
host.services.software:(vendor:"GitLab" and product:"GitLab") or web.software:(vendor:"GitLab" and product:"GitLab")
risks.name={`Vulnerable GitLab Server (CVE-2026-85706)`,`Vulnerable GitLab Server (CVE-2026-87719)`}