CVE-2026-84411 is a critical integer underflow in the HTTP request body handling of MikroTik RouterOS’s web management service (CVSS 3.1 9.8) that lets a remote, unauthenticated attacker execute arbitrary code as root or cause a denial of service with a single crafted HTTP request. No authentication, user interaction, or special privileges are required to reach the vulnerable code path. The only technical account published so far is CISA’s ICS advisory (ICSA-26-272-06), which names the affected component as RouterOS’s web management service without further detail; as of October 5, 2026, MikroTik has not published its own advisory for this CVE. Censys currently detects RouterOS’s web management interface broadly exposed to the Internet; version is observable on most instances, but the vulnerable-version boundary for RouterOS’s older 6.x long-term branch has not been identified (see Affected Assets).
Details
| Field | Description |
| CVE-ID | CVE-2026-84411, CVSS 3.1 9.8 (Critical), assigned via CISA/ICS-CERT coordination |
| Date of Disclosure | September 29, 2026 |
| Affected Assets | MikroTik RouterOS devices exposing the web management (WebFig) HTTP interface |
| Vulnerable Software Versions | 7.x branch: before 7.246.x branch: unconfirmed |
| PoC Available | No, as of this writing. |
| Exploitation Status | Not confirmed. Not listed in the CISA KEV catalog as of this writing; CISA’s advisory states no known public exploitation has been reported. |
| Patch Status | Fixed in RouterOS 7.24, available at MikroTik Software Downloads |
Affected Assets
CISA’s ICS advisory states that RouterOS versions before 7.24 are affected and that 7.24 or later resolves the issue. MikroTik operates two parallel release lines: a current 7.x branch and an older 6.x long-term-support branch that remains in active use on a large share of deployed devices. CISA’s wording tracks the 7.x versioning scheme, and MikroTik’s own advisory page does not list this CVE at all as of this writing, so whether the 6.x branch shares the underlying flaw, and if so what build fixes it, is not established from public sources yet. This advisory does not assume either answer.
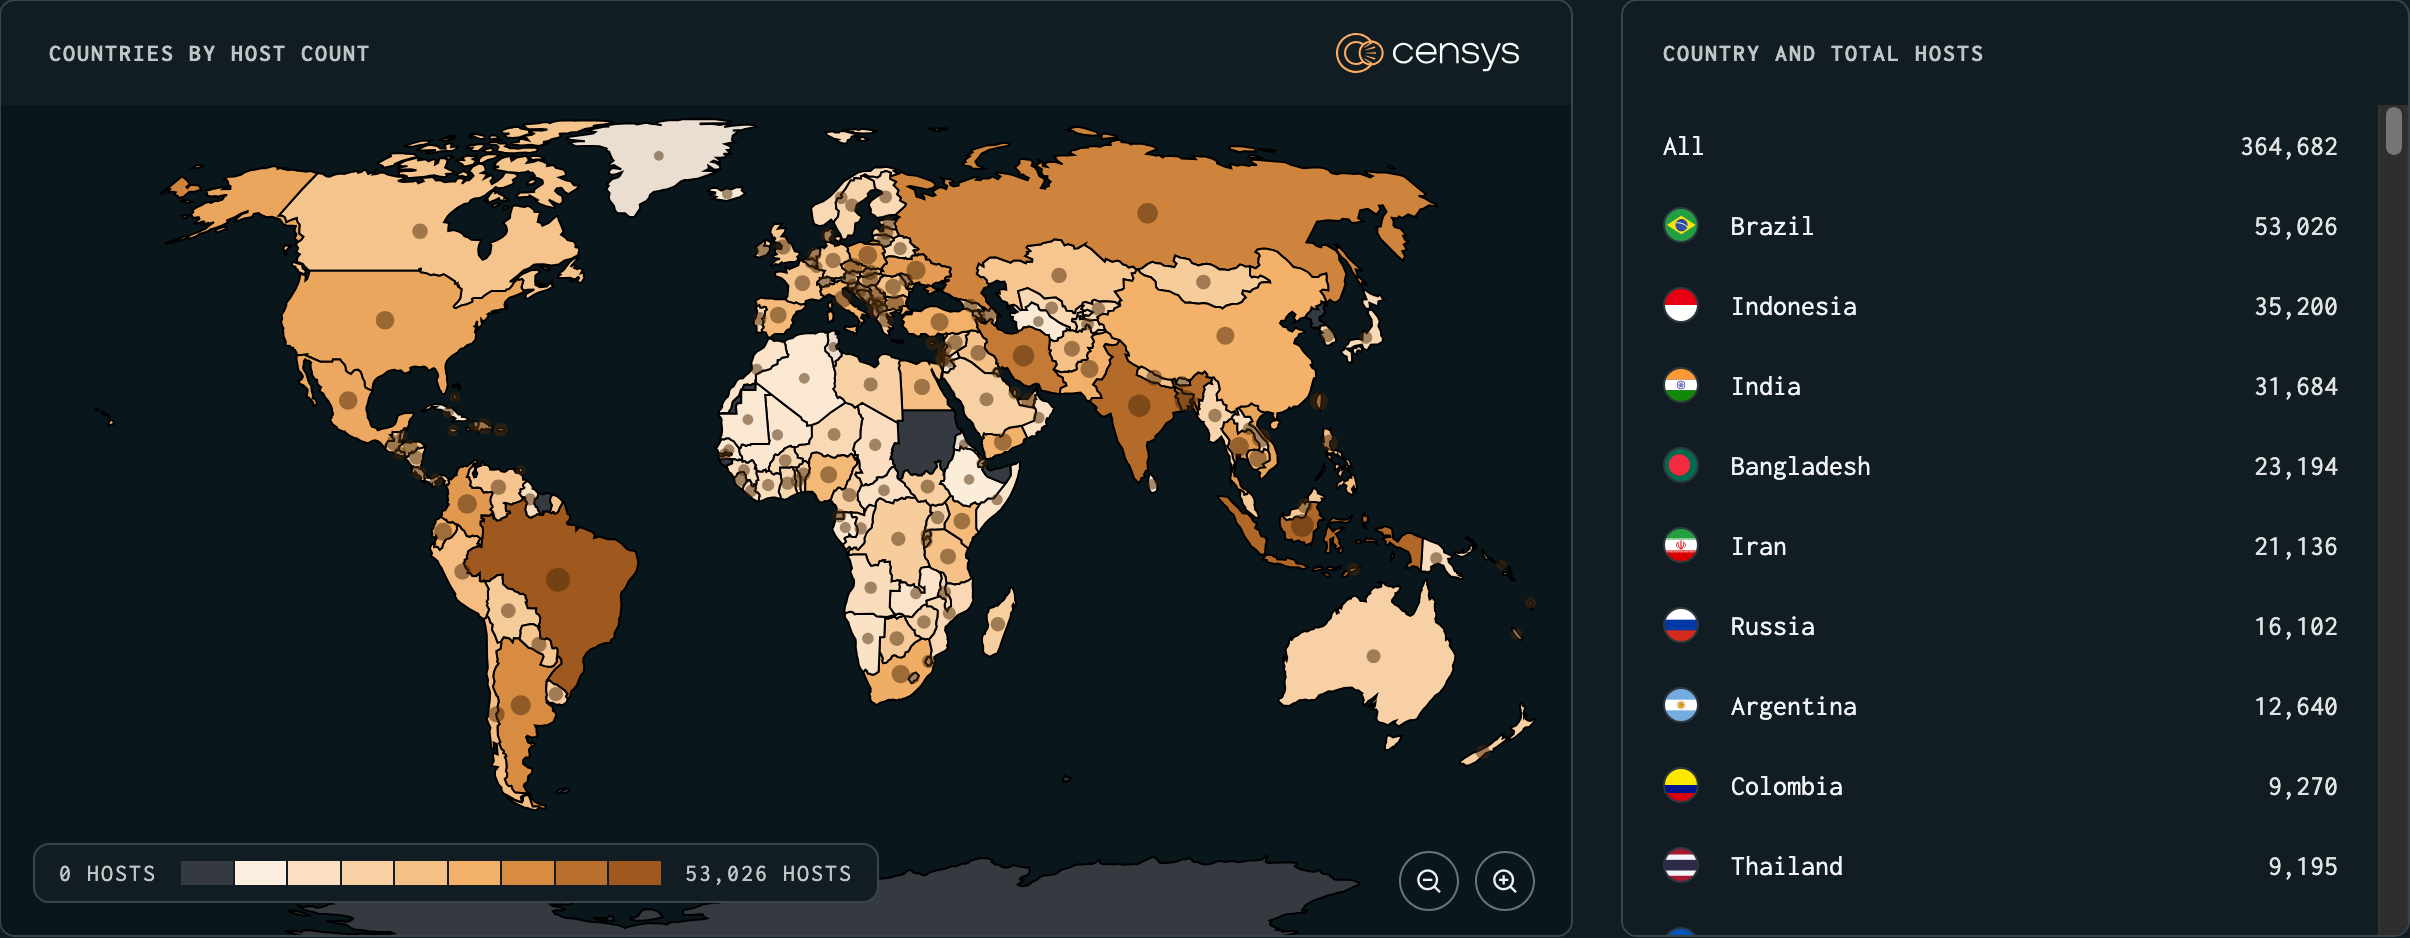
Censys currently detects 364,341 hosts and 439,624 web properties identified as MikroTik RouterOS and exposing the web management login page. Of the hosts, roughly 19,200 report a 7.x version string and roughly 328,500 report a 6.x version string in the page body, with the remainder reporting a version string that did not match either prefix. None of the hosts reporting a 7.x version report the patched 7.24 release or later as of October 5, 2026.
Censys Query
We currently detect 364,341 hosts running RouterOS’s web management interface, based on the following query:
host.services: (operating_systems:(vendor="mikrotik" and product="routeros") and endpoints.http.html_title="RouterOS router configuration page")
Censys also detects 439,624 web properties exposing the same interface, based on the following query against the web-property index:
web.operating_systems:(vendor="mikrotik" and product="routeros") and web.endpoints.http.html_title="RouterOS router configuration page"
These queries match RouterOS’s own software identification together with the web management login page, confirming both that the product is identified and that the specific surface this CVE is in is reachable. They still reflect product exposure broadly, not a vulnerable-version filter: the 6.x/7.x branch split above means a meaningful share of these hosts may not be affected by this specific CVE, pending MikroTik’s own advisory.
PoC Available?
No public proof-of-concept or exploit code has been identified for CVE-2026-84411 as of October 5, 2026.
Exploitation Status
CVE-2026-84411 is not listed in the CISA Known Exploited Vulnerabilities (KEV) catalog as of October 5, 2026. CISA’s ICS advisory states that no known public exploitation has been reported to CISA at the time of publication. There is no independent sensor or researcher reporting of in-the-wild exploitation as of this writing.
Patch Status
MikroTik fixed CVE-2026-84411 in RouterOS 7.24, available from MikroTik Software Downloads. Administrators running the 7.x branch should upgrade to 7.24 or later. Adoption of the fix appears to be at or near zero as of October 5, 2026: Censys detects no instance, anywhere on the 7.x branch, reporting the patched release. Administrators running the 6.x long-term branch should check MikroTik Security Advisories directly for an updated advisory before assuming either that the branch is unaffected or that a specific 6.x build resolves it: as of October 5, 2026, MikroTik had not published that determination.
Devices exposing the web management interface to the Internet without a compensating control (VPN, management-network allowlisting) should restrict that access regardless of patch status, since this reduces exposure to any future vulnerability in the same component.
References
- NVD: CVE-2026-84411 (CVE record)
- CISA ICS Advisory ICSA-26-272-06 (affected/fixed version guidance, exploitation status)
- MikroTik Security Advisories (vendor advisory page, does not yet list this CVE as of this writing)
- MikroTik Software Downloads (fixed release)
- CWE-191: Integer Underflow (weakness class)