Vulnerability Description
CVE-2026-84295 is a critical (CVSS v3.1 10.0) improper authentication vulnerability in Progress WS_FTP Server on Windows. According to Progress, it “could allow an unauthenticated remote attacker to access sensitive information, including administrative credentials.” Progress’s record lists the impact as an authentication bypass that may enable further compromise of the server, and does not name the affected service. The record lists versions prior to 2024.0.6 and 2025.0.3 as affected.
Progress disclosed six more WS_FTP Server vulnerabilities the same day, all listed as affecting versions prior to 2024.0.7 and 2025.0.4. CVE-2026-90868 (CVSS v3.1 9.9) is an OS command injection that could allow arbitrary command execution under certain configurations, and it is the most severe of the six. The other five score 8.1 to 9.1. Three of them (CVE-2026-90863, CVE-2026-90864, and CVE-2026-90866) describe a delegated Host Administrator exceeding their authorized scope, and two of those could lead to arbitrary command execution or remote code execution. CVE-2026-90865 is a second OS command injection under certain configurations, and CVE-2026-90867 is improper access control in the Web Admin console that could expose administrative functionality to remote authentication attempts.
The two sets have different floors. Per Progress’s CVE records, WS_FTP Server 2024.0.7 and 2025.0.4 are the first builds outside the affected range of all seven. Progress’s release notes for 2024.0.7 and 2025.0.4 list those builds without naming the CVEs. Builds 2024.0.6 and 2025.0.3 fall outside the CVE-2026-84295 range and inside the range of the other six, so a server upgraded only for the CVSS 10 is still listed as affected. Progress’s records advise restricting network access to the Web Admin console to trusted administrative hosts, limiting the Host Administrator role to trusted staff, auditing virtual folder paths, and contacting Progress Technical Support for further mitigations.
Impact
CVE-2026-84295 could give an unauthenticated attacker the administrative credentials of a WS_FTP Server. Of the related flaws, three could let a delegated Host Administrator reach files outside their scope or run commands on the underlying Windows server, and the two OS command injection flaws could allow command execution under certain configurations. A credential an attacker has already read stays valid after the upgrade, so an instance that was reachable while unpatched warrants rotating its administrative credentials, including delegated Host Administrator accounts, once the upgrade is done.
Details
| CVE | CVE-2026-84295 (CVSS v3.1 10.0, critical); CVE-2026-90863 through CVE-2026-90868 (8.1 to 9.9); assigned and scored by Progress Software |
| Date of Disclosure | October 29, 2026 |
| Affected Assets | Progress WS_FTP Server on Windows |
| Vulnerable Software Versions | CVE-2026-84295: prior to 2024.0.6 and 2025.0.3. CVE-2026-90863 through CVE-2026-90868: prior to 2024.0.7 and 2025.0.4 |
| PoC Available | No public proof-of-concept has been identified as of October 29, 2026 |
| Exploitation Status | No exploitation has been reported as of October 29, 2026 |
| Patch Status | Per the CVE records, 2024.0.7 and 2025.0.4 or later are outside the affected range of all seven; 2024.0.6 and 2025.0.3 are outside the CVE-2026-84295 range only; release date not stated by the vendor |
Censys ARC Perspective
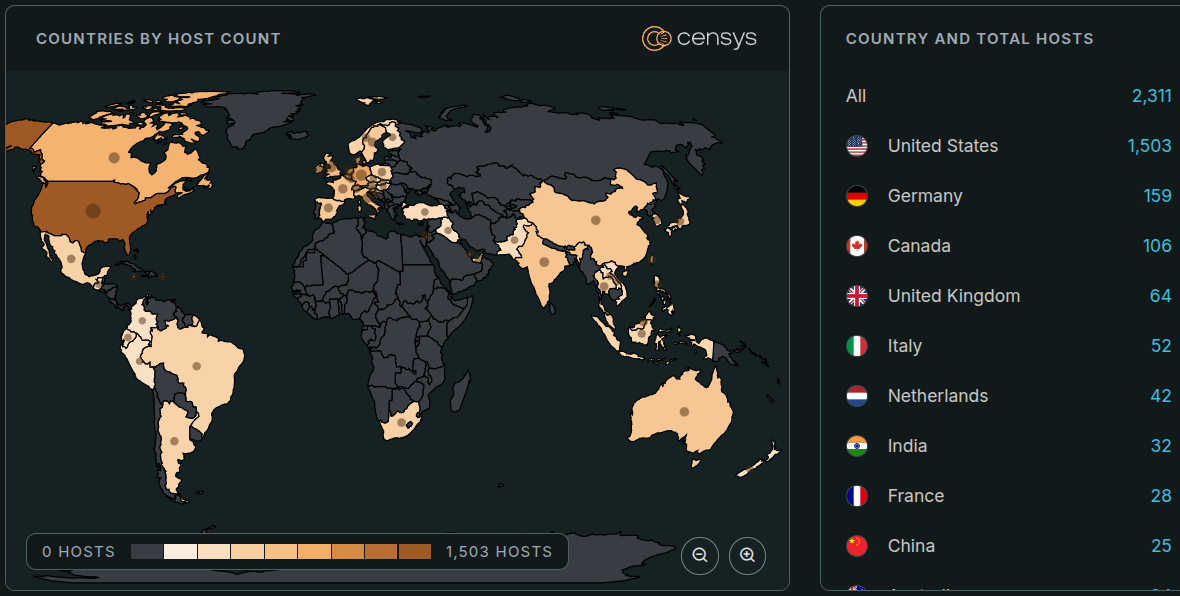
Censys observes roughly 2,500 hosts running WS_FTP Server and resolves the build number on nearly all of them, which shows how far the fixes have spread. Of roughly 1,000 hosts on the 2024 and 2025 release lines, a little over half still run a build below the fixes for the six related vulnerabilities, and the rest already run a fixed build. About 60 percent of all the hosts, roughly 1,500, report only releases from before the 2024 line. The CVE records give those ranges no lower bound, so older releases fall inside them as written.
The Censys ARC team notified customers of potentially vulnerable instances in their attack surfaces. These figures cover Internet-reachable instances as of October 29, 2026.
Censys Queries
Platform: Found: 2,515 hosts
host.services.software:(vendor="ipswitch" and product="ws_ftp") or host.services.banner:"WS_FTP"
ASM:
host.services.software:(vendor="Ipswitch" and product="WS_FTP") or web_entity.instances.software:(vendor="Ipswitch" and product="WS_FTP") or host.services.banner: "WS_FTP"