Vulnerability Description
CVE-2026-77876 is a critical (CVSS v3.1 9.8) OS command injection in the protected_directory module of the Control Web Panel (CWP) user panel. According to NVD, “Control Web Panel (CWP) before webpanel_version 1.16 contains an OS command injection vulnerability in the protected_directory user panel module that allows attackers to execute arbitrary commands by submitting unescaped input through the file POST parameter in the acc=deletedp action. Attackers can exploit this flaw, which passes attacker-controlled input directly into a shell_exec call, to achieve code execution in the user panel context.” NVD’s description states no authentication requirement and no configuration precondition, and lists releases before 1.16 as affected.
Three more CWP user panel flaws were disclosed the same day. CVE-2026-73696 (CVSS v3.1 9.1) is an authentication bypass, caused by a missing exit() after a redirect, that NVD says lets unauthenticated attackers reach user panel functionality; it affects releases before 1.12. CVE-2026-73695 (CVSS v3.1 8.8) is a path traversal that allows local PHP file inclusion, and CVE-2026-73697 (CVSS v3.1 8.8) is an arbitrary file write and command injection that requires access to the phpini_editor module. Both affect releases before 1.16.
NVD does not describe the four vulnerabilities as a chain, so each is a separate route to either code execution or access in the user panel. Although CVE-2026-77876 has the highest CVSS score, CVE-2026-73696 is the only vulnerability NVD describes as reachable without authentication.
The vendor has published no advisory for any of the four. Its changelog names none of the CVEs and has no 1.16 entry as of November 2, 2026, so the 1.12 and 1.16 boundaries come from NVD alone. The changelog’s 1.26 entry (October 26, 2026) describes command injection fixes in other user panel modules and its 1.27 entry (October 30, 2026) describes a security review of the admin panel, so the build that closed each flaw may differ from the NVD boundary.
Impact
NVD describes arbitrary command execution in the user panel context. No public exploit code has been identified for CVE-2026-77876 as of November 2, 2026, so there is no demonstrated post-exploitation behavior to report. CWP is a web hosting control panel, and a server running it holds hosted websites, databases, and mail accounts, which command execution in the panel context puts at risk. Upgrading closes the flaws but does not undo any earlier access. No indicators of compromise have been published for these CVEs, so an instance that was reachable on an affected release has no published artifact to check against and warrants a general review for unexpected files and processes.
Details
| CVE | CVE-2026-77876 (CVSS v3.1 9.8, Critical) CVE-2026-73696 (9.1, Critical) CVE-2026-73695 (8.8, High) CVE-2026-73697 (8.8, High) |
| Date of Disclosure | November 2, 2026 |
| Affected Assets | Control Web Panel (CWP), formerly CentOS Web Panel, user panel. NVD lists no other products |
| Vulnerable Software Versions | CVE-2026-77876, CVE-2026-73695, CVE-2026-73697: before 1.16. CVE-2026-73696: before 1.12 |
| PoC Available | None identified as of November 2, 2026. |
| Exploitation Status | No exploitation reported as of November 2, 2026 |
| Patch Status | The vendor’s changelog names none of the CVEs. Version 1.30.1, released November 3, 2026, is the current release and is above every release NVD lists as affected. |
Censys ARC Perspective
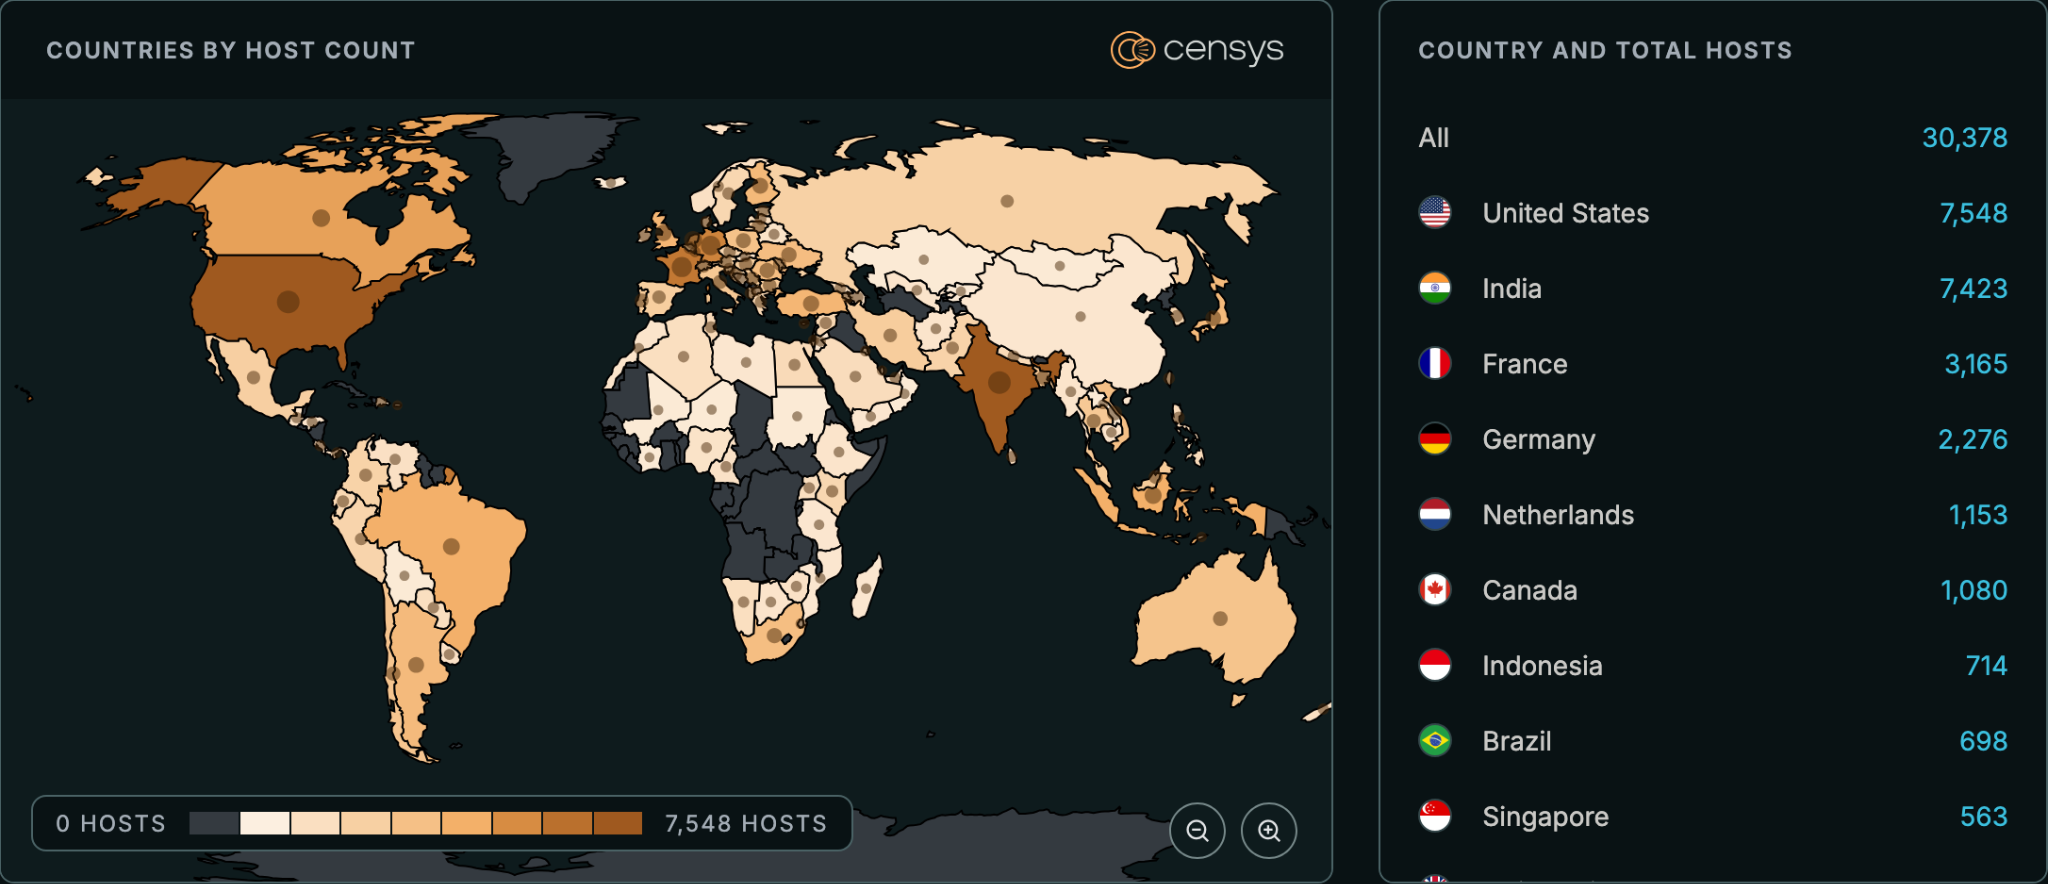
Censys observes roughly 440,000 web properties running Control Web Panel as of November 2, 2026. The release is not readable from scan data, so that figure is an upper bound on the vulnerable population. The Censys ARC team notified customers of potentially vulnerable instances in their attack surfaces.
The population is commodity hosting. About half of the hosts are in the United States and India, and nearly half sit with five hosting providers and VPS operators, so exposure is concentrated with the operators who run CWP for their customers. About 60% of hosts also answer on the user panel ports, which the CWP wiki lists as 2082 and 2083 and where all four flaws sit. Figures cover Internet-reachable instances as of November 2, 2026.
Censys Queries
Platform: Found: 443,734 web properties
web.software:(vendor="control-webpanel" and product="webpanel")
ASM:
host.services.software:(vendor="Control Web Panel" and product={"Control Web Panel","WebPanel"}) or web_entity.instances.software:(vendor="Control Web Panel" and product={"Control Web Panel","WebPanel"})