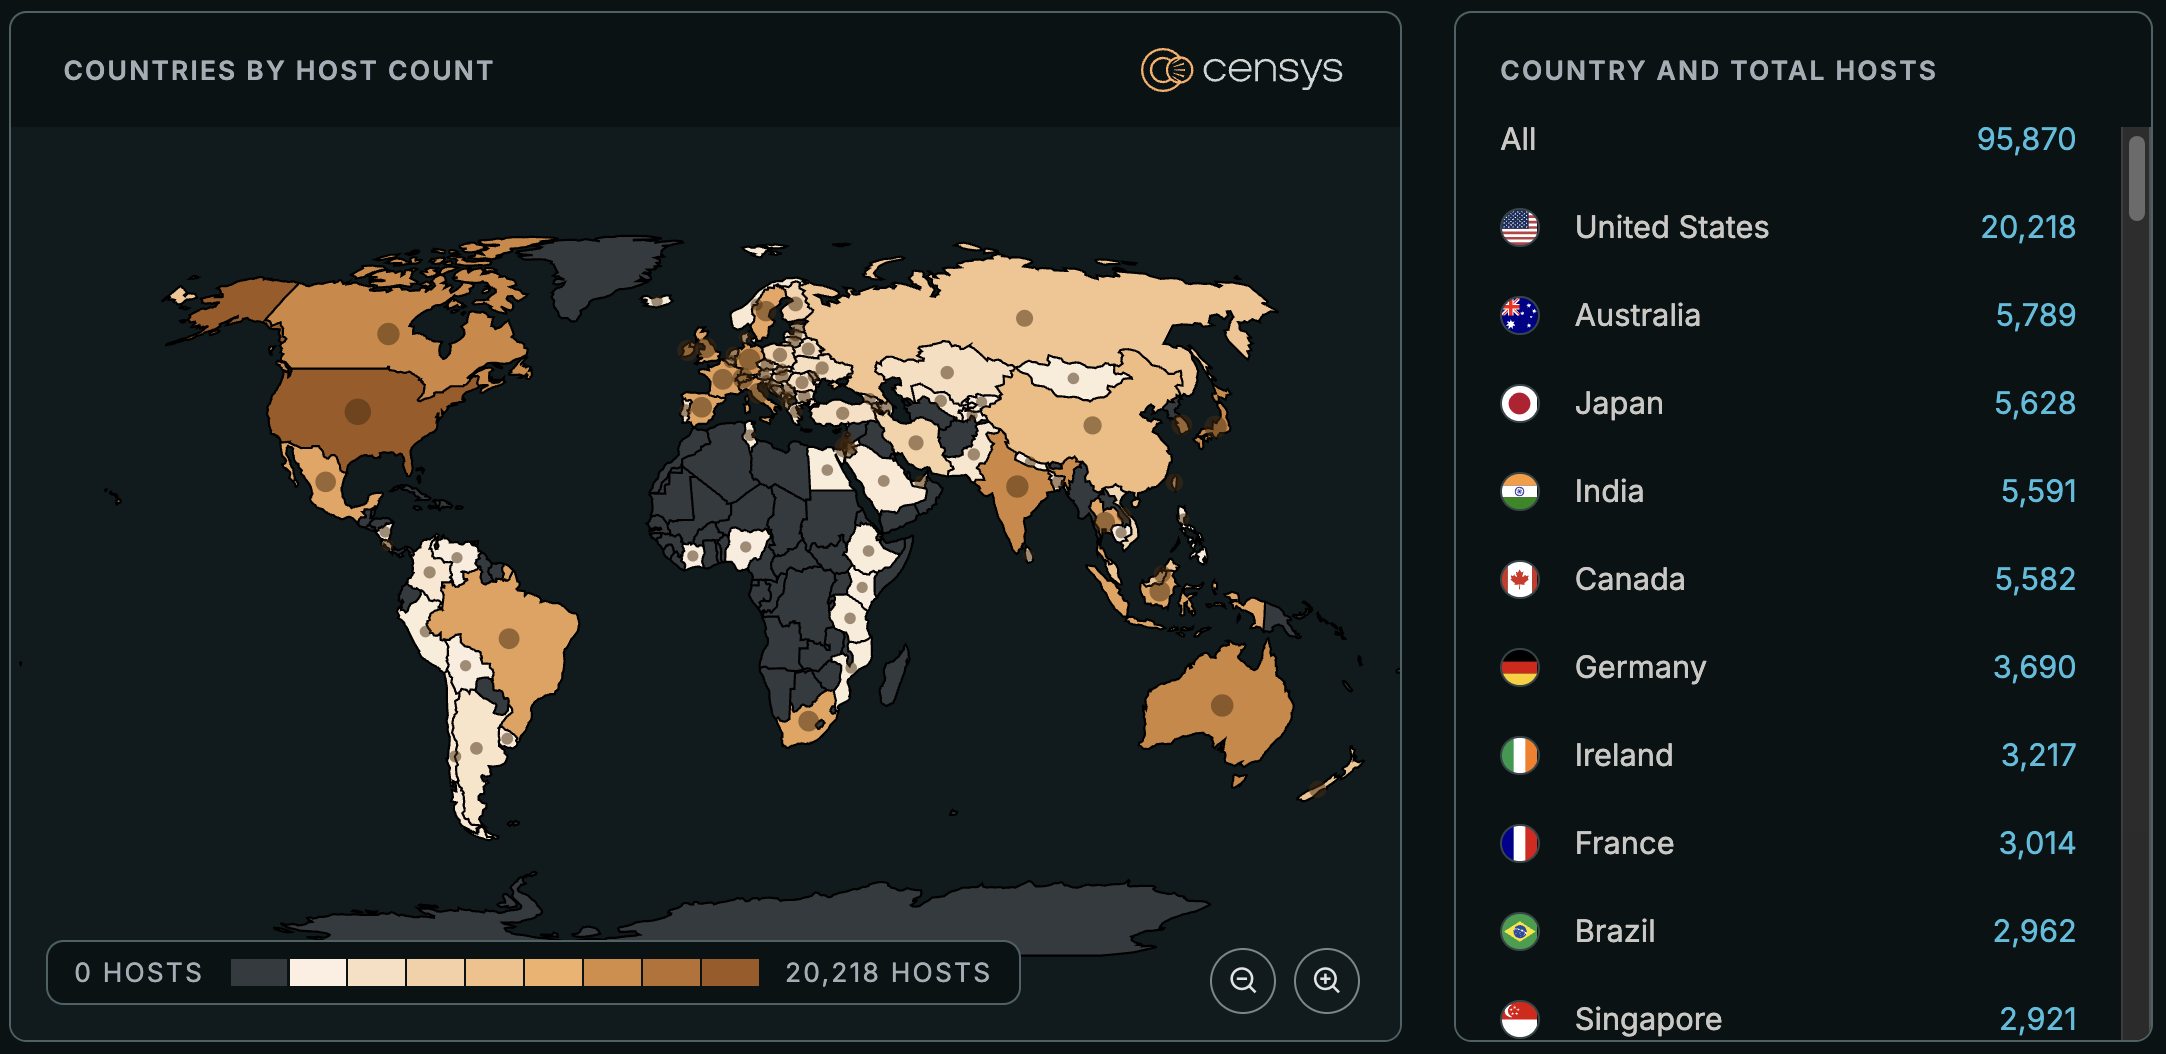
CVE-2026-21589 is an unauthenticated file-access vulnerability (CVSS 9.3) affecting eight Atlassian Data Center products at once: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Per Atlassian’s advisory, the flaw lets a remote, unauthenticated attacker read specific files inside the web application root directory using path traversal sequences (.. adjacent to /, \, or ::, including URL-encoded variants). Censys currently observes well over one hundred thousand internet-facing hosts, and a separate, larger population of web properties, running the affected products; see Censys Query below for the full counts and query.
Details
| Field | Description |
| CVE-ID | CVE-2026-21589, CVSS v4.0 9.3 (Critical), assigned by Atlassian |
| Date of Disclosure | October 5, 2026 |
| Affected Assets | Data Center deployments of Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Atlassian Cloud is explicitly not affected; Atlassian has already applied the fix there and cloud customers need take no action |
| Vulnerable Software Versions | All versions before the fixed builds listed in Patch Status, across all eight products |
| PoC Available | No, as of October 7, 2026 |
| Exploitation Status | Not confirmed. Not listed in the CISA Known Exploited Vulnerabilities (KEV) catalog as of October 7, 2026 |
| Patch Status | Atlassian released fixed builds for all eight products on October 5, 2026; see Patch Status below for per-product versions |
Affected Assets
Censys currently detects 95,366 hosts and 431,502 web properties running the affected products, after excluding assets Censys labels as honeypots. The unfiltered counts are 135,855 hosts and 535,112 web properties; roughly 30 percent of the raw host count and 19 percent of the raw web-property count carry a honeypot label, so this is a meaningfully contaminated space and the honeypot-excluded figures are the ones to treat as representative of real deployments. The host and web indexes are populated independently and are not reported as one combined figure, since the two overlap (the same instance can appear in both). See Censys Query below for the query.
Censys Query
Due to the number of products, it’s quite long, but we generated the numbers based on the following query:
(
  web.software:(vendor="atlassian" and product={"bitbucket","bamboo"})
  or web.endpoints:(
    http.html_title={"Log in - Bitbucket","Log into Atlassian - BitBucket","Atlassian Crowd - Login"}
    or http.html_title=~"^(System Dashboard - |Log.{0,3}n - Jira)"
    or http.html_title=~"^(Fisheye|Log in to (Fisheye|Fisheye and Crucible|Crucible)) [0-9]+[.][0-9]+[.][0-9]+$"
    or http.favicons.hash_md5="2fa69f2bc9174ffc21fc3c7925da6862"
    or (http.headers:(key="X-Confluence-Request-Time") and http.html_title:"Confluence")
  )
  or host.services.software:(vendor="atlassian" and product={"bitbucket","bamboo"})
  or host.services:(
    endpoints.http.html_title={"Log in - Bitbucket","Log into Atlassian - BitBucket","Atlassian Crowd - Login"}
    or endpoints.http.html_title=~"^(System Dashboard - |Log.{0,3}n - Jira)"
    or endpoints.http.html_title=~"^(Fisheye|Log in to (Fisheye|Fisheye and Crucible|Crucible)) [0-9]+[.][0-9]+[.][0-9]+$"
    or endpoints.http.favicons.hash_md5="2fa69f2bc9174ffc21fc3c7925da6862"
    or (endpoints.http.headers:(key="X-Confluence-Request-Time") and endpoints.http.html_title:"Confluence")
  )
) and not labels:"HONEYPOT"
PoC Available?
No public proof-of-concept exploit code has been identified for CVE-2026-21589 as of October 7, 2026.
Exploitation Status
CVE-2026-21589 is not listed in the CISA Known Exploited Vulnerabilities (KEV) catalog as of October 7, 2026, and no exploitation in the wild has been reported by any national CERT or security vendor as of October 7, 2026.
Patch Status
Atlassian released fixed versions for all eight affected products on October 5, 2026, documented in Atlassian’s advisory:
- Bitbucket Data Center: fixed in 9.4.26, 10.2.8, or 10.5.1
- Confluence Data Center: fixed in 9.2.26 or 10.2.19
- Crowd Data Center: fixed in 6.3.7, 7.0.3, 7.1.7, or 7.2.4
- Jira Software Data Center: fixed in 9.12.40, 10.3.26, or 11.3.12
- Jira Service Management Data Center: fixed in 5.12.40, 10.3.26, or 11.3.12
- Bamboo Data Center: fixed in 10.2.24 or 12.1.12
- Crucible: fixed in 4.9.15
- Fisheye: fixed in 4.9.15
Each product maintains parallel release branches; compare a deployed build against the fixed version for its own branch rather than against the highest version number listed, since a newer-looking release on a different branch is not necessarily patched.
Where upgrading immediately is not possible, Atlassian’s advisory provides a Web Application Firewall rule to block requests matching the path-traversal pattern, a Tomcat RewriteValve configuration (WEB-INF/rewrite.config) for Confluence, Jira Software, Jira Service Management, Bamboo, and Crowd, and a urlrewrite.xml rule for Bitbucket. Atlassian frames these as limiting exposure rather than remediating the underlying flaw; applying the fixed version remains the only complete remediation.
Because the flaw can expose files containing database credentials, any instance that was internet-reachable and unpatched should have those credentials rotated after upgrading. A credential read before patching remains valid after patching, so upgrading alone does not revoke access to a secret an attacker already obtained.