[CVE-2026-121805, CVE-2026-116953, CVE-2026-120285, CVE-2026-120292, CVE-2026-120722, CVE-2026-123637]
Vulnerability Description
CVE-2026-121805, CVE-2026-116953, CVE-2026-120285, CVE-2026-120292, CVE-2026-120722, and CVE-2026-123637 are vulnerabilities in the Traffic Management Microkernel (TMM) of F5 BIG-IP, and in BIG-IP Next for Kubernetes and BIG-IP Next CNF for some of them, that let a remote, unauthenticated attacker crash TMM and may lead to remote code execution. F5, as the CVE Numbering Authority, scored each CVSS v3.1 9.8, classified each as a stack-based buffer overflow (CWE-121), and published them on November 18, 2026.
In 2020, F5 recommended that the BIG-IP TMUI web interface be reachable only from a secure or out-of-band network, not directly from the Internet (F5 article K13092), as CERT/CC recorded in its note on CVE-2020-5902, a remote command execution flaw in that interface. These six are different: F5 describes them as data plane issues with no control plane exposure, and the data plane is where a BIG-IP handles client traffic, which makes it the part more likely to face the Internet.
F5’s CVE records describe each flaw in a single sentence. For CVE-2026-121805, F5’s CVE record says: “When an iRule that processes client traffic using the PEM::subscriber command is configured on a virtual server, undisclosed requests can cause the Traffic Management Microkernel (TMM) to terminate and may lead to remote code execution (RCE).“
Each of the six requires one of the following on a virtual server, per F5:
- An iRule that processes client traffic using
PEM::subscriber(CVE-2026-121805, F5 advisory K000163946) - An iRule that processes client traffic using
GENERICMESSAGE::route(CVE-2026-116953, F5 advisory K000163941) - An HTTP profile and an iRule containing
PSC::ip_address(CVE-2026-120285, F5 advisory K000163939) - An HTTP profile and an iRule using the
MR::message routecommand (CVE-2026-120292, F5 advisory K000163940) - An iRule that processes client traffic using
DNS::scrape(CVE-2026-120722, F5 advisory K000163945) - BIG-IP APM provisioned, with a per-request policy that includes the Client Information agent and Endpoint Security agents (CVE-2026-123637, F5 advisory K000163937)
F5’s CVE records also name an affected module for three of the iRule CVEs: PEM for CVE-2026-121805 and CVE-2026-120285, and DNS for CVE-2026-120722. The records do not say whether that module must be provisioned for the flaw to apply.
Each CVE has its own trigger, and the fixed builds for each BIG-IP line cover all six. F5 describes each as a data plane issue with no control plane exposure. F5 published other lower-scored BIG-IP CVEs on the same day, which this advisory does not cover. These six are separate from CVE-2026-94127, a BIG-IP APM remote code execution flaw that F5 disclosed on September 22, 2026 and that CISA lists in its Known Exploited Vulnerabilities (KEV) catalog.
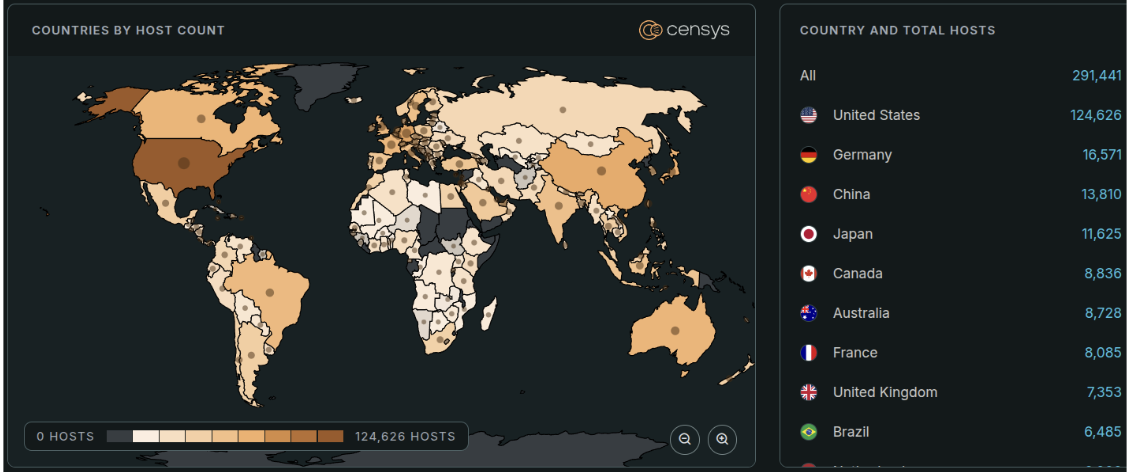
Hosts with an F5 BIG-IP detection, from a Platform host search. A host is one IP address, so this count is lower than the web property figure under Censys Queries, which counts every hostname and port.
Impact
F5 states that traffic is disrupted while TMM restarts and that exploitation may lead to remote code execution. F5’s CVE records list no workaround for any of the six, and list fixed builds for each affected line.
Details
| CVE | CVE-2026-121805, CVE-2026-116953, CVE-2026-120285, CVE-2026-120292, CVE-2026-120722, CVE-2026-123637: CVSS v3.1 9.8 Critical each, assigned by F5 as CNA |
| Date of Disclosure | November 18, 2026 |
| Affected Assets | Per F5’s CVE records of November 18, 2026: F5 BIG-IP for all six. BIG-IP Next for Kubernetes for the five iRule CVEs (not CVE-2026-123637). BIG-IP Next CNF for CVE-2026-121805, CVE-2026-120285, and CVE-2026-120722. F5 did not evaluate versions past End of Technical Support. |
| Vulnerable Software Versions | BIG-IP 21.1, 17.5, and 17.1 lines, from 21.1.0, 17.5.0, and 17.1.0 until the fixed build; F5’s records give no upper bound. BIG-IP Next for Kubernetes and BIG-IP Next CNF 2.4, 2.3, and 2.2 lines, from 2.4.0, 2.3.0, and 2.2.0 until the fixed build. |
| PoC Available | None found as of November 18, 2026. |
| Exploitation Status | No exploitation reported as of November 18, 2026. |
| Patch Status | The builds F5 lists as fixed: BIGIP-21.1.0.4.0.19.3-ENG (21.1.0), BIGIP-17.5.1.11.0.61.12-ENG or BIGIP-17.5.1.10.0.80.35-ENG (17.5.0), BIGIP-17.1.3.7.0.21.4-ENG or BIGIP-17.1.3.6.0.14.20-ENG (17.1.0), BNK-2.4.2-EHF1 (2.4.0), BNK-2.3.4-EHF1 (2.3.0), BNK-2.2.5-EHF1 (2.2.0) for both Next for Kubernetes and Next CNF, per F5’s CVE records of November 18, 2026. F5 amended some records that day, so confirm against F5’s advisories. |
Censys Queries
Platform: Found: 2,067,455 web properties
web.software:(vendor="f5" and product={"big-ip_ltm","big-ip_application_security_manager","big-ip_advanced_waf","big-ip_configuration_utility"})
ASM:
host.services.software:(vendor="F5" and product={"BIG-IP Configuration Utility","Big-IP Application Security Manager","BIG-IP Advanced WAF Software","BIG-IP LTM"}) or web_entity.instances.software:(vendor="F5" and product={"BIG-IP Configuration Utility","Big-IP Application Security Manager","BIG-IP Advanced WAF Software","BIG-IP LTM"})