Vulnerability Description
CVE-2026-88771 is an improper input validation vulnerability (CWE-20) in Citrix NetScaler ADC and Citrix NetScaler Gateway, “leading to an unauthenticated attacker to execute arbitrary commands” (NVD). CVE-2026-88772 is a memory buffer vulnerability (CWE-119) in the same products “leading to Remote Code Execution or Denial of Service” (NVD). Citrix and CISA confirm both were exploited as zero-days. The same Citrix bulletin covers six further CVEs (CVE-2026-88773 through CVE-2026-88778), none reported as exploited; this advisory focuses on the two that each independently enable remote code execution.
According to the Dutch National Cyber Security Centre (NCSC-NL), CVE-2026-88771 affects all NetScaler ADC and Gateway deployments and requires no additional functionality or specific configuration. That makes it unlike most recent NetScaler vulnerabilities, which required the appliance to be configured as a Gateway or AAA virtual server. CVE-2026-88772 is exploitable only when DTLS is enabled, which NCSC-NL notes is the default on VPN virtual servers.
watchTowr published a root-cause analysis of CVE-2026-88771. By watchTowr’s account, attacker-controlled request data written to the appliance’s logs is later interpolated into a shell command by the ns_monuploadd_err.pl error-handling script, and the injected command runs when that script executes, which watchTowr reports can be up to 24 hours after the request.
Details
| Field | Description |
| CVE-ID | CVE-2026-88771, CVSS 4.0: 9.5 (Critical, Citrix), CVSS 3.1: 9.8 (Critical, NVD). CVE-2026-88772, CVSS 4.0: 9.5 (Critical, Citrix), CVSS 3.1: 8.1 (High, NVD) |
| CVSS Vectors | CVE-2026-88771: CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H; CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:HCVE-2026-88772: CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H; CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Date of Disclosure | September 27, 2026 (NVD and Citrix bulletin CTX697096) |
| Affected Assets | Citrix NetScaler ADC and Citrix NetScaler Gateway, including FIPS and NDcPP builds |
| Vulnerable Software Versions | 14.1 before 14.1-73.37; 13.1 before 13.1-64.23; 14.1-FIPS before 14.1-73.37; 13.1-FIPS and 13.1-NDcPP before 13.1-37.279; end-of-life 12.1 and 13.0 (no fix) |
| PoC Available | Yes for CVE-2026-88771 (watchTowr); none known for CVE-2026-88772 as of September 28, 2026 |
| Exploitation Status | Exploited in the wild as zero-days; both added to the CISA Known Exploited Vulnerabilities (KEV) catalog on September 27, 2026 |
| Patch Status | Citrix published fixed builds in bulletin CTX697096 |
Affected Assets
Per NVD and the Citrix bulletin (CTX697096), the following are affected:
- NetScaler ADC and NetScaler Gateway 14.1: before 14.1-73.37, fixed in 14.1-73.37
- NetScaler ADC and NetScaler Gateway 13.1: before 13.1-64.23, fixed in 13.1-64.23
- NetScaler ADC 14.1-FIPS: before 14.1-73.37, fixed in 14.1-73.37
- NetScaler ADC 13.1-FIPS and 13.1-NDcPP: before 13.1-37.279, fixed in 13.1-37.279
TThe FIPS and NDcPP builds follow a separate release cadence: the 13.1-FIPS and NDcPP fix is build 37.279, not 64.23, so a single 13.1 build number cannot be applied across a mixed fleet.
NetScaler ADC and NetScaler Gateway 12.1 and 13.0 are end-of-life and receive no fix. Appliances on those branches must be upgraded to a supported branch.
Censys Query
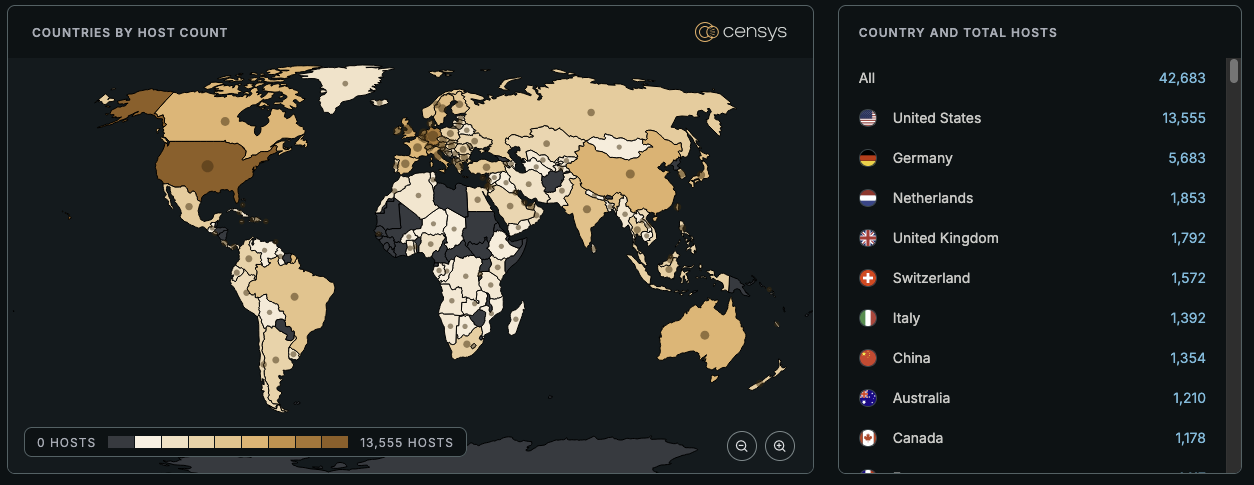
We currently detect NetScaler ADC or NetScaler Gateway running on 42,735 hosts and 323,527 web properties as of September 28, 2026. These are total exposed instances, not confirmed-vulnerable counts, and the two figures are different units that should not be added together.
host.services.software:(vendor:"citrix" and product:"netscaler") or
host.services.software:(vendor:"citrix" and product:"gateway")web.software:(vendor:"citrix" and product:"netscaler") or web.software:(vendor:"citrix" and product:"gateway")The whole population is potentially in scope. For recent NetScaler vulnerabilities, such as CVE-2026-19490 in August, the first analytical step was narrowing the population to the configuration the flaw required, typically a Gateway or AAA virtual server. That step does not apply here. NCSC-NL states that CVE-2026-88771 requires no specific configuration, so every one of the 42,735 hosts should be treated as exposed until its build is confirmed as fixed. The Gateway subset, 40,751 hosts, is also where CVE-2026-88772’s precondition applies by default, since DTLS is on by default for VPN virtual servers.
Population shape. The United States accounts for 13,549 hosts (32%), followed by Germany at 5,678 (13%), then the Netherlands, United Kingdom, and Switzerland at roughly 4% each. Microsoft hosts 4,254 (10%) and Amazon 3,013 (7%), consistent with NetScaler VPX virtual appliances deployed in public cloud. More than three quarters of hosts sit outside the ten largest networks, spread across enterprise and telecom address space.
Baseline for tracking takedowns. The Gateway host population stood at 41,338 on August 19, 2026 and 40,751 on September 28, 2026. With Citrix and national CERTs advising administrators to take appliances offline or restrict access, this figure is the baseline against which removals from the internet can be measured over the coming days.
PoC Available?
Yes, for CVE-2026-88771. watchTowr has published a technical analysis and a Detection Artifact Generator that demonstrates the injection path. Both are linked from the watchTowr writeup.
No public proof-of-concept is known for CVE-2026-88772 as of September 28, 2026.
Exploitation Status
Both CVEs are exploited in the wild.
- CISA added CVE-2026-88771 and CVE-2026-88772 to KEV on September 27, 2026, with a remediation due date of September 30, 2026. CISA’s alert states that “threat actors are actively exploiting these vulnerabilities globally.”
- NCSC-NL confirms active exploitation of both CVEs.
- Tenable reports that the first public reports of exploitation surfaced on September 25, 2026, and that watchTowr confirmed exploitation on September 26, 2026, before a patch or CVE was published.
The CVSS v3.1 score of 8.1 that NVD assigns CVE-2026-88772 understates its risk. It is confirmed exploited, and the precondition it depends on is a default setting.
Patch Status
Citrix has released fixed builds in bulletin CTX697096 (see Affected Assets). Remediation, in order:
- Before patching, check for compromise and preserve evidence. CISA warns that “updates may result in loss of forensic visibility.” NCSC-NL advises securing logs and memory dumps before updating.
- Upgrade to a fixed build. Appliances on 12.1 or 13.0 must move to a supported branch.
- Run a compromise assessment on any appliance that was internet-exposed and unpatched on or after September 25, 2026, regardless of its current patch state. Patching does not remove persistence an attacker already installed.
Citrix provides indicators of compromise through NetScaler Console (version 14.1-73.36 or later, with telemetry enabled), or on request from Citrix Support for customers without Console. Citrix notes these indicators may not cover all threat actor tactics, techniques, and procedures. Citrix’s guidance “Steps to Take if NetScaler ADC is Suspected to be Compromised” (CTX694799) covers response steps. For CVE-2026-88771, watchTowr reports that injected payloads appear in syslog alongside “AAAD API: sending login req” and process_kernel_socket messages; review syslog for shell metacharacters in logged login fields and User-Agent values.
References
- NVD: CVE-2026-88771 (CVSS vectors, CWE-20, affected versions)
- NVD: CVE-2026-88772 (CVSS vectors, CWE-119, affected versions)
- Citrix Security Bulletin CTX697096 (vendor advisory: CVE-2026-88771 through CVE-2026-88778, affected and fixed builds)
- CISA KEV: CVE-2026-88771 (added September 27, 2026, due September 30, 2026)
- CISA alert: Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway (active exploitation, forensic-preservation guidance)
- NCSC-NL advisory NCSC-2026-0394 (per-CVE preconditions, exploitation confirmation)
- Canadian Centre for Cyber Security AL26-024 (national CERT alert)
- CERT-EU advisory 2026-014 (national CERT alert)
- watchTowr: CVE-2026-88771 analysis (root cause, Detection Artifact Generator)
- Tenable FAQ (disclosure timeline, end-of-life branch status)