Vulnerability Description
CVE-2026-103039 is a PHP object injection in the Gravity Forms plugin for WordPress, versions 3.1.2 and earlier, with a CVSS v3.1 score of 9.8 assigned by Wordfence, the CVE Numbering Authority. An unauthenticated attacker can inject a PHP object into the site’s post meta. According to the CVE record, “This is due to GFFormsModel::create_post() passing the submitted value to WordPress’ unrestricted global maybe_unserialize() rather than the plugin’s own hardened GFCommon::maybe_unserialize(), which was added in 3.1.1 and passes allowed_classes => false precisely to prevent object instantiation.“
The vulnerable path is reachable only through a Post Custom Field whose input type is List, and the CVE record says the submitted row reaches the unserialize call verbatim where the field has a content template enabled. Neither setting is visible from outside the site.
The injected object does nothing by itself, because the plugin contains no gadget chain. The CVE record names two ways to supply one. Another plugin or theme on the site can provide a chain. Or, where the custom field is mapped to the protected _wp_page_template meta key, WordPress itself supplies the chain, and on hosts with a readable PEAR install and register_argc_argv enabled that yields remote code execution.
Impact
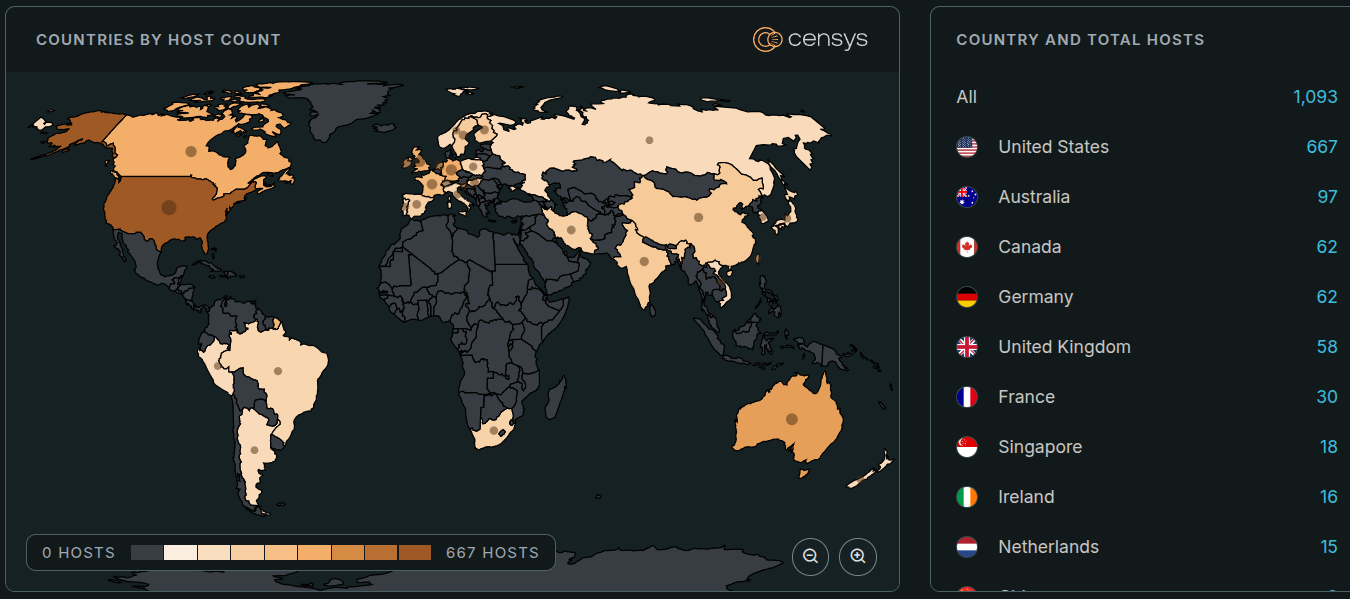
As of this publication, no public exploit code has been identified. The CVE record describes the outcome: a successful request leaves an attacker-controlled PHP object in the site’s post meta, and on a site where a gadget chain is available that becomes remote code execution on the host. Whether a given site has a usable chain depends on its other plugins and themes and on host settings that Censys cannot observe. Updating Gravity Forms removes the injection point.
Details
| CVE | CVE-2026-103039, CVSS v3.1 9.8 Critical (Wordfence, the CNA) |
| Date of Disclosure | October 29, 2026 (Patchstack); October 30, 2026 (NVD) |
| Affected Assets | Gravity Forms plugin for WordPress, on forms with a Post Custom Field of the List input type and a content template |
| Vulnerable Software Versions | 3.1.2 and earlier |
| PoC Available | No public proof-of-concept has been identified as of October 30, 2026. |
| Exploitation Status | No confirmed exploitation as of October 30, 2026; the CISA assessment in the CVE record rates exploitation as none. Patchstack labels the flaw as known to be exploited without naming a source. |
| Patch Status | Patchstack lists 3.1.3 as the patched version, released October 2, 2026; the vendor’s release post does not name the CVE. |
Censys Queries
Platform: Found: 83,800 web properties
web.software:(vendor="rocketgenius" and product="gravityforms")
ASM:
host.services.software:(vendor:"rocketgenius" and product:"gravityforms") or web_entity.instances.software:(vendor:"rocketgenius" and product:"gravityforms")