Vulnerability Description
CVE-2026-101767 is a critical (CVSS v3.1 9.8) unauthenticated vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite. Oracle’s description reads: “Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in takeover of Oracle Application Object Library.” Oracle tests only releases under Premier Support or Extended Support, and says it is likely that earlier versions of the affected releases are also affected.
Oracle’s description does not name the mechanism. Horizon3.ai, who discovered the flaw, describes the vulnerable endpoint as the Thin Client Framework servlet at /OA_HTML/AppsTCFServer and the flaw as an unauthenticated SQL injection that runs as the APPS database user. It states that the endpoint is permitted through the default EBS URL firewall configuration and that Internet-facing web tiers present the most direct exposure. Horizon3.ai reported the flaw to Oracle on July 24, 2026, and Oracle fixed it in the October 20, 2026 Critical Patch Update.
Horizon3.ai’s interim mitigations are to remove /OA_HTML/AppsTCFServer (implemented by oracle.apps.fnd.tcf.SocketServer) from the URL firewall allowlist and restrict the web tier to trusted networks. They narrow the attack surface without fixing the flaw. Its indicators of compromise are unauthenticated POST requests to /OA_HTML/AppsTCFServer that instantiate the class oracle.apps.jtf.gantt.server.GanttDataServer, followed by backend database activity; database reconnaissance (database version, current user, and directory objects) shortly afterward; unexpected files in $APPLPTMP; and the oracle account spawning /bin/sh through the Concurrent Manager.
Oracle reports 194 new security patches for E-Business Suite in this update, out of 1,295 across all product families. Oracle says 31 of the E-Business Suite vulnerabilities in the update may be remotely exploitable without authentication. Oracle also recommends applying the same update to the Oracle Database and Oracle Fusion Middleware components of E-Business Suite.
The same update fixes CVE-2026-101809, a CVSS v3.1 10.0 unauthenticated flaw in the Workflow Notification Mailer component of Oracle Workflow that affects the same versions. This advisory covers CVE-2026-101767, which Horizon3.ai has described in a technical writeup.
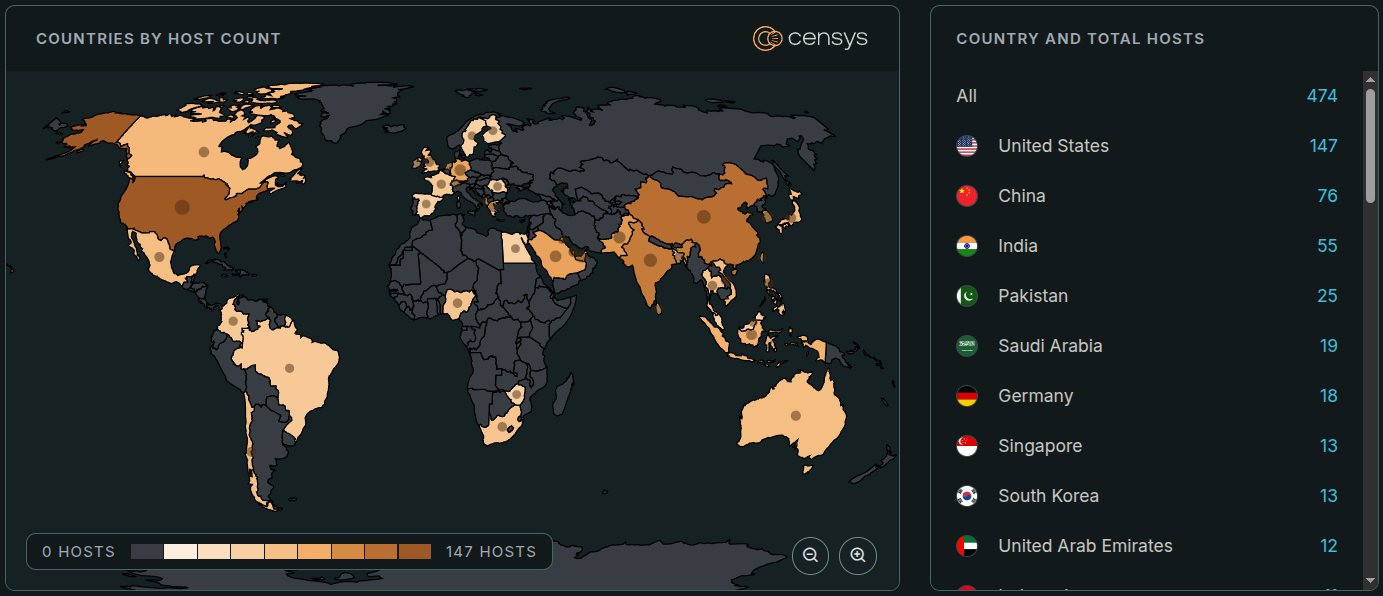
Scan data does not show which E-Business Suite instances run an affected release or have applied the October 2026 update, so the queries below find instances that run the product, not vulnerable ones.
Impact
Horizon3.ai reports that the SQL injection can be chained to operating system command execution as the EBS application account, which would extend the compromise from the database to the application host. Applying the October 2026 Critical Patch Update is the only complete remediation. An Internet-facing instance that was unpatched should be reviewed for the indicators of compromise outlined above.
Details
| CVE | CVE-2026-101767, CVSS v3.1 9.8 Critical, assigned by Oracle |
| Date of Disclosure | October 20, 2026 |
| Affected Assets | Oracle E-Business Suite, Oracle Application Object Library (component: Core) |
| Vulnerable Software Versions | 12.2.3 through 12.2.15 |
| PoC Available | Horizon3.ai has developed a validation test for the flaw. |
| Exploitation Status | No reports of exploitation in the wild identified as of October 27, 2026. |
| Patch Status | Fixed in Oracle’s October 2026 Critical Patch Update, released October 20, 2026. The patches that apply to an installation are listed in My Oracle Support Note KA923. |
Censys Queries
Platform: Found 2,246 web properties
web.software:(vendor="oracle" and product="e-business_suite") and not labels:"HONEYPOT"
ASM:
host.services.software:(vendor="Oracle" and product="E-Business Suite") or web_entity.instances.software:(vendor="Oracle" and product="E-Business Suite")