CVE-2026-123007, CVE-2026-123633, CVE-2026-123634, CVE-2026-121810, CVE-2026-113425
Vulnerability Description
Ten vulnerabilities in F5 NGINX Open Source and NGINX Plus were disclosed on November 18, 2026, five of which have been dubbed “nginx2root“ and warrant the most attention. F5 rates each 8.1 (High) under CVSS v3.1 and 9.2 (Critical) under CVSS v4.0.
On their own, each NGINX flaw could allow a remote, unauthenticated attacker to corrupt memory in an NGINX worker process when a set of specific features are enabled – leading to code execution where ASLR is disabled or the attacker can bypass it. Reaching root on the host requires chaining one of these with a separate Linux kernel flaw, which has no patch yet.
The five flaws are all independent, and each needs a different feature to be in use:
| CVE | Severity (nginx.org) | Affected Open Source Versions | Affected configuration | Trigger | Memory flaw |
| CVE-2026-123007 | Major | 1.9.5–1.30.6 1.31.0–1.31.8 | HTTP/2 enabled | Undisclosed traffic pushes the flow control window past its limit | Heap buffer overflow, typically followed by a worker segfault |
| CVE-2026-113425 | Major | 0.5.33–1.30.6 1.31.0–1.31.8 | Mail proxy (per Xint, with proxy on and auth_http) | Undisclosed traffic during login; no valid credentials needed | Use-after-free |
| CVE-2026-123633 | Medium | 1.19.7–1.30.6 1.31.0–1.31.8 | HTTP/2 client connections proxied to a backend, with a worker low on worker_connections | Crafted request | Use-after-free |
| CVE-2026-123634 | Medium | 0.6.18–1.30.6 1.31.0–1.31.8 | resolver, a proxied server name containing variables, and an SSI or mirror subrequest resolving the same name | Crafted HTTP request | Use-after-free |
| CVE-2026-121810 | Medium | 1.25.0–1.30.6 1.31.0–1.31.8 | HTTP/3 (QUIC) proxied to a backend, with a worker low on worker_connections | Remote, unauthenticated traffic; also depends on conditions outside the attacker’s control | Use-after-free, leading to a worker restart |
The most immediate risk likely comes from CVE-2026-123007, which is likely to have the broadest impact since it needs only HTTP/2. Wiz demonstrated leveraging it to gain remote code execution, complete with an ASLR bypass, against official 1.31.7 and 1.31.8 builds, and Rapid7 has published a proof of concept for the same flaw. Note however that this doesn’t look like a plug-and-play exploit: Rapid7 says it needs roughly 128 GB of HTTP/2 traffic and was built against a single test setup.
What an attacker can do largely depends on what they chain together: on its own each CVE leads to code execution, but Xint chained CVE-2026-123007 with a Linux kernel flaw, which is in the Linux SCTP subsystem, to reach root on the host. The chain also worked from inside a Docker container.
All five are fixed in 1.30.7 (stable) and 1.31.9 (mainline). Compare your build against the fix for your own branch: 1.31.8 is affected while 1.30.7 is not, even though 1.31.8 is the higher number. For NGINX Plus, use the fixed release named in F5’s advisory for each CVE.
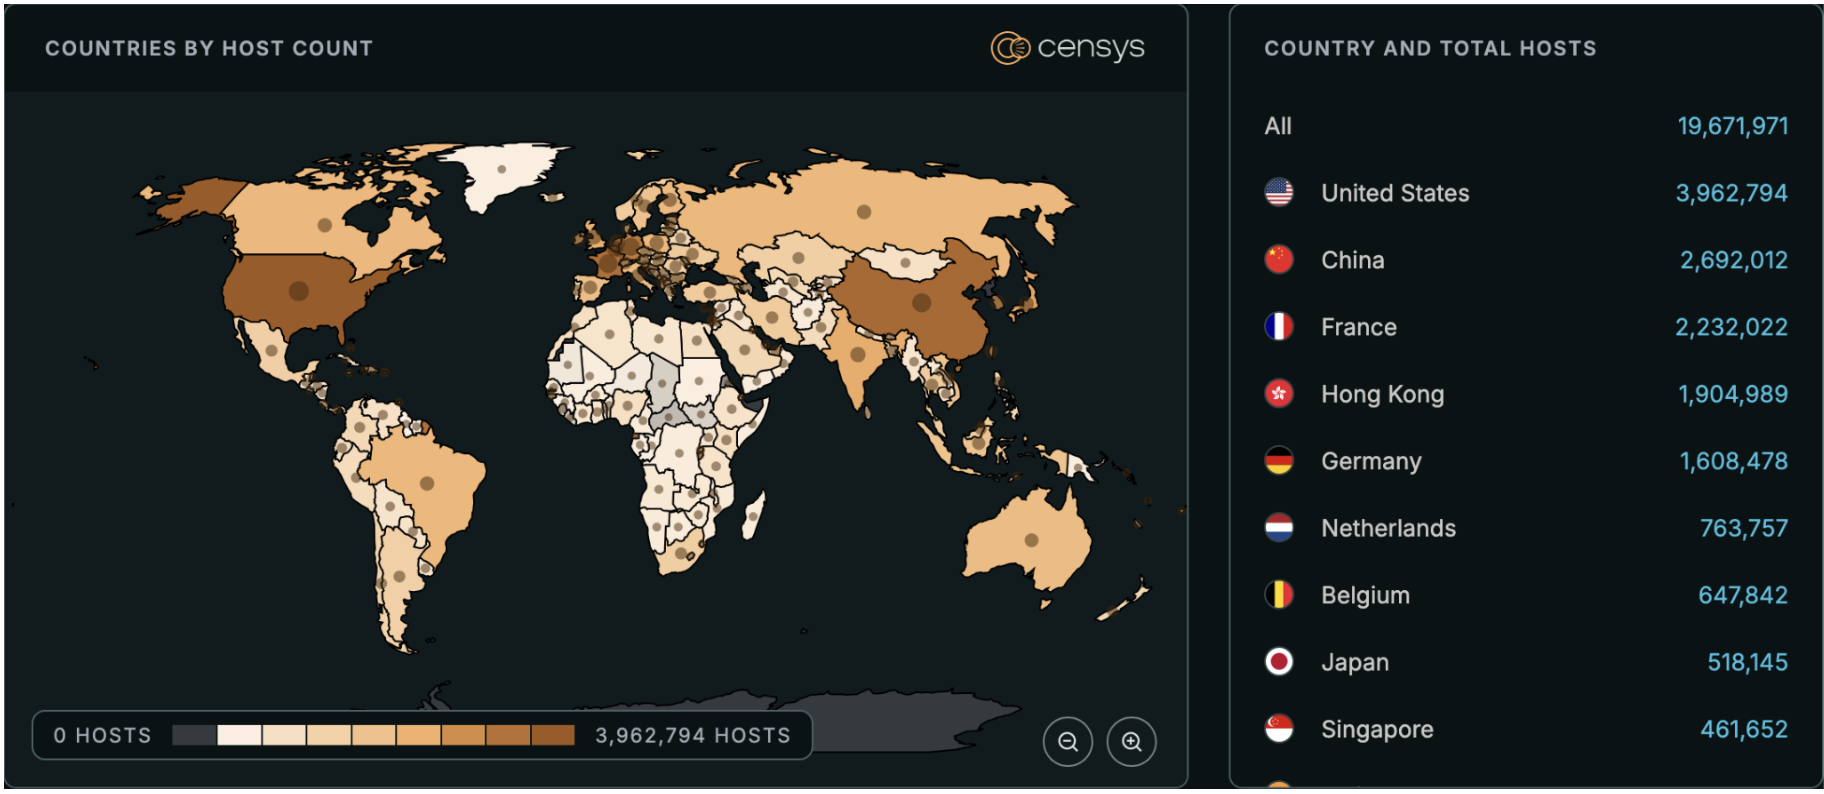
Hosts running NGINX, from a Platform host search. A host is one IP address, so this count is lower than the web property figure below, which counts every hostname and port.
Details at a Glance
| CVE | CVE-2026-123007, CVE-2026-123633, CVE-2026-123634, CVE-2026-121810, and CVE-2026-113425. F5 assigned each CVSS v3.1 8.1 (High) and CVSS v4.0 9.2 (Critical) |
| Date of Disclosure | November 18, 2026 |
| Affected Assets | F5 NGINX Open Source and NGINX Plus, in certain configurations; see table above for more details. |
| Vulnerable Software Versions | NGINX Open Source per nginx.org, from the version listed through 1.31.8: CVE-2026-123007 from 1.9.5; CVE-2026-123633 from 1.19.7; CVE-2026-123634 from 0.6.18; CVE-2026-121810 from 1.25.0; CVE-2026-113425 from 0.5.33. Stable releases 1.30.7 and later are not vulnerable. NGINX Plus per F5’s advisories. |
| PoC Available | Rapid7 has published a proof of concept for CVE-2026-123007 only. Wiz Research states it will not release its exploits at this time, and Xint omitted the final steps of its exploits from public reporting. |
| Exploitation Status | The Censys ARC team is not aware of exploitation in the wild as of November 18, 2026. |
| Patch Status | NGINX Open Source: fixed in 1.30.7 (stable) and 1.31.9 (mainline), both released November 18, 2026. NGINX Plus: 37.0.8.1 and 37.3.0.1 fix all five. F5 lists no fixed build for R36 and earlier. |
| Interim Mitigation | Disabling HTTP/2 blocks CVE-2026-123007 and CVE-2026-123633 only |
Censys Queries
Platform: All internet-exposed NGINX: 331,242,037 web properties
web.software:(vendor = "f5" and product = "nginx")
and not web.labels.value = "HONEYPOT"
Platform: Affected versions of NGINX: 74,183,698 web properties
web.software: (
vendor = "f5" and product = "nginx" and (
(version >= "0.5.33" and version <= "1.30.6")
or version =~ `^1[.][4-9][.]`
or (version >= "1.31.0" and version <= "1.31.8")
)
) and not web.labels.value = "HONEYPOT"
ASM:
risks.name="Vulnerable nginx with HTTP/2 [nginx2root]"
If an instance was reachable with an affected feature enabled before it was patched, it is worth a closer look. Start with processes launched by the worker user, which Xint calls the clearest sign of a successful attack, and then check the NGINX error logs for repeated worker exits, keeping in mind that these can also have benign causes. Access logs will not help with CVE-2026-123007, because the HTTP/2 control frames it relies on are not logged as requests.
References
- nginx.org security advisories
- F5 advisory for CVE-2026-123007
- F5 advisory for CVE-2026-123633
- F5 advisory for CVE-2026-123634
- F5 advisory for CVE-2026-121810
- F5 advisory for CVE-2026-113425
- NVD: CVE-2026-123007
- NVD: CVE-2026-123633
- NVD: CVE-2026-123634
- NVD: CVE-2026-121810
- NVD: CVE-2026-113425
- Wiz Research: NGINX HTTP/2 vulnerabilities
- Xint: nginx2root