Vulnerability Description
CVE-2026-108097 is a remote code execution vulnerability in the Field UI module of Drupal core, covered by Drupal security advisory SA-CORE-2026-014. Drupal describes it as “A remote code execution vulnerability exists within the Field UI module in Drupal core.” Drupal rates it Critical, scoring it 19 out of 25 on its own risk scale.
Core alone is not directly exploitable. Drupal says multiple exploit paths exist with contributed modules, at least one of which does not require authentication, and that custom code may also expose the vulnerable functionality. Drupal does not name the modules. Its mitigation is to uninstall the field_ui module.
Fortbridge published a technical write-up on October 18, 2026, linking its lab repository. The lab reproduced the chain without authentication against Drupal 11.4.9, using a module Fortbridge specifically wrote to supply attacker input. Fortbridge reports that the vulnerable code is removed in 11.4.10 and that its exploit variants fail against it. Fortbridge searched public contributed modules and found the only one using the vulnerable pattern was Entity List, which Drupal fixed in 3.0.10 under SA-CONTRIB-2026-218 as CVE-2026-108099.
Fortbridge indicates that real exposure is more likely to sit in custom modules written for individual sites. It lists a copied settings.php or a new .php file under sites/default/files/, and any change to files/.htaccess, as signs of compromise.
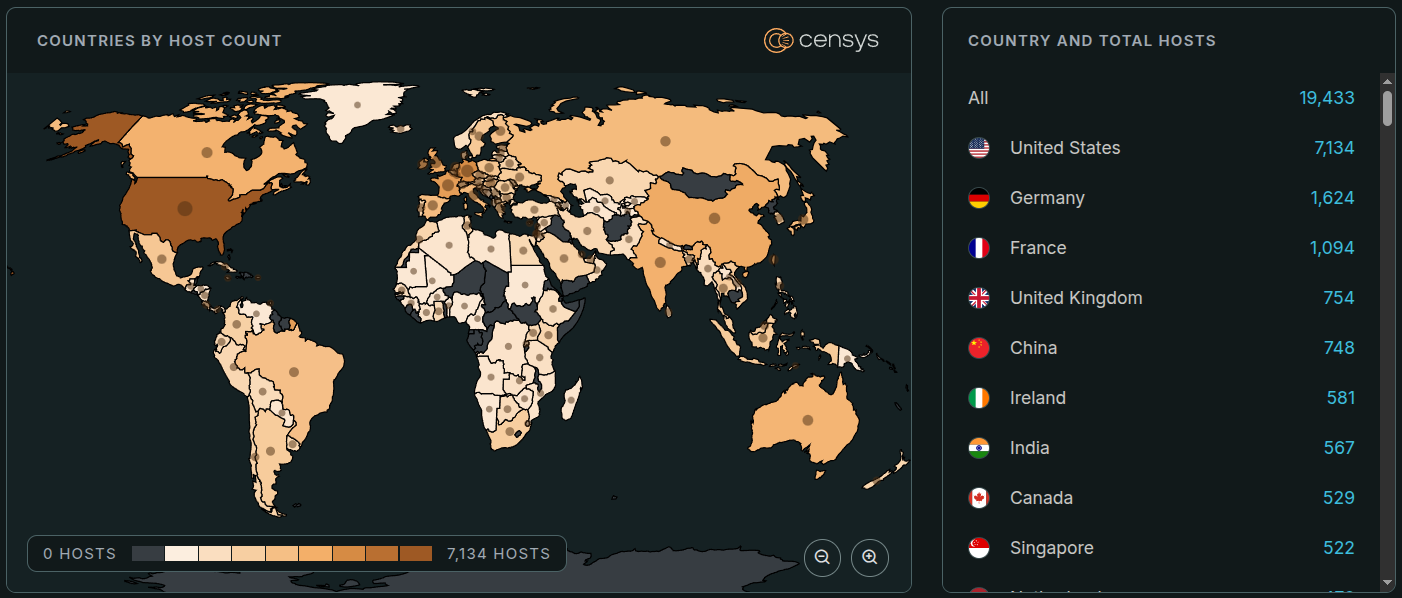
Hosts running Drupal, from a Platform host search. A host is one IP address, so this count is lower than the web property figure below, which counts every hostname and port.
Impact
Where a module or custom code passes attacker input to the vulnerable code, Fortbridge’s lab chain runs code as the web server user and copies the site’s settings file, which holds the database credentials and hash salt. A site in that position that was reachable while unpatched should treat those credentials as exposed, rotate them, and review the site for signs of use, in addition to upgrading.
Details
| CVE | CVE-2026-108097; Drupal rating Critical (19/25); no CVSS score published |
| Date of Disclosure | October 14, 2026 |
| Affected Assets | Drupal core within the ranges below, with a contributed module or custom code that reaches the vulnerable code; Drupal 7 and earlier are not mentioned |
| Vulnerable Software Versions | 8.9.0 before 10.6.19; 11.0.0 before 11.3.19; 11.4.0 before 11.4.10; 12.0.0-alpha1 before 12.0.0-beta2 |
| PoC Available | Yes, a public write-up with its lab repository from Fortbridge (October 18, 2026); the chain needs a module Fortbridge wrote |
| Exploitation Status | No exploitation in the wild has been reported as of October 29, 2026 |
| Patch Status | Fixed in Drupal 10.6.19, 11.3.19, and 11.4.10 (October 14, 2026); Drupal 12.0.0-beta2 is outside the affected range; no fix is listed for end-of-life branches; mitigation is uninstalling field_ui |
Censys Queries
Platform: Found: 1,476,471 web properties
web.software:(vendor="drupal" and product="drupal") and not labels:"HONEYPOT"
ASM:
host.services.software:(vendor:"drupal" and product:"drupal") or web_entity.instances.software:(vendor:"drupal" and product:"drupal")