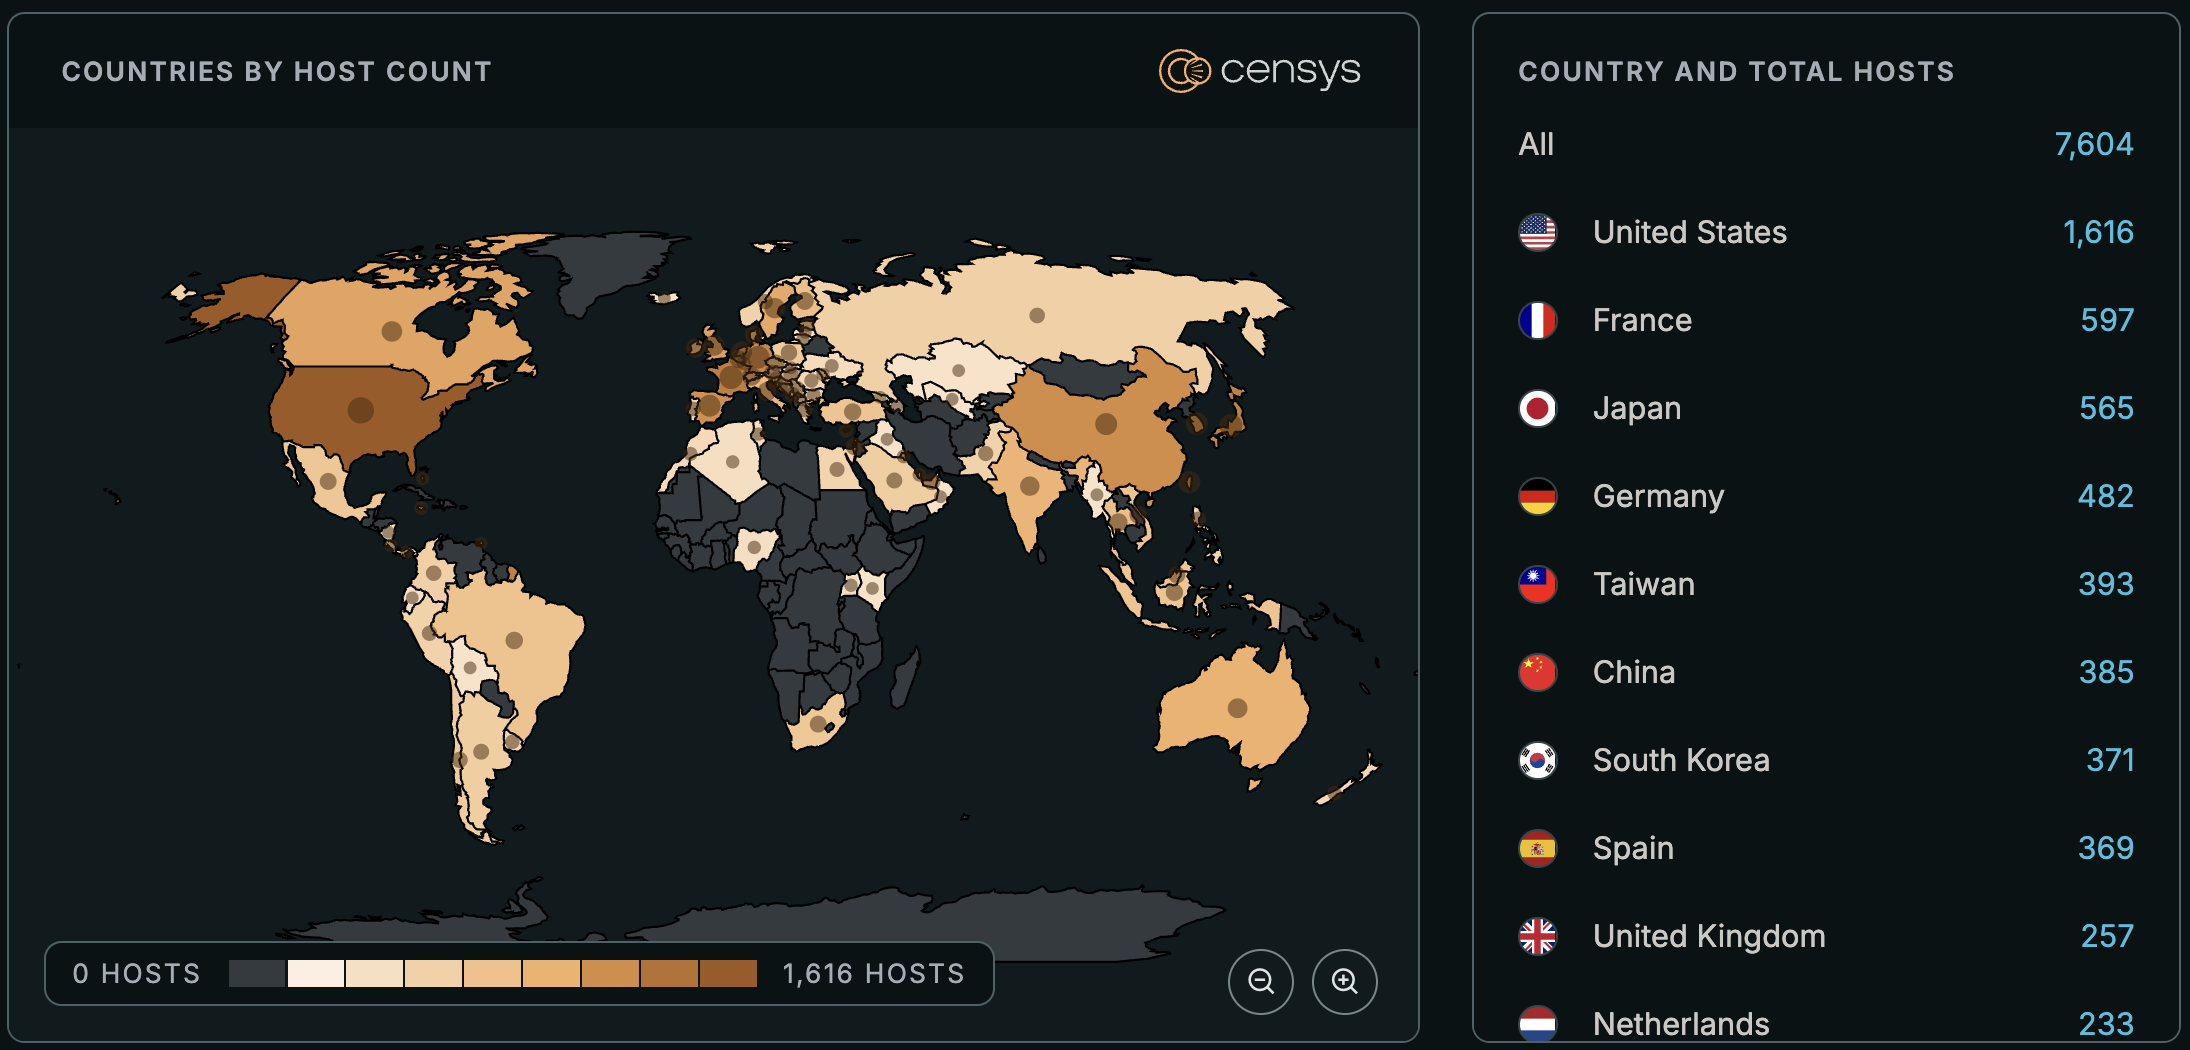
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure, CVSS 8.6, that allows a remote, unauthenticated attacker to execute arbitrary commands. Ivanti states it is aware of exploitation in the wild affecting a limited number of customers, and Volexity reports the attacker chained this flaw with a privilege escalation vulnerability that Ivanti had not yet patched. CISA added it to its Known Exploited Vulnerabilities (KEV) catalog on October 13, 2026, the day NVD published the CVE. Censys currently observes 7,604 hosts and 269,319 web properties with Ivanti Connect Secure, excluding honeypots.
Details
| CVE-ID | CVE-2026-104935. CVSS 3.1 8.6 (High) |
| Date of Disclosure | October 13, 2026 |
| Affected Assets | Ivanti Connect Secure on the 25.1 and 22.8R2 branches. NVD states that 22.7R2.14 and prior are not impacted. |
| Vulnerable Software Versions | 25.1.1.1 and prior 25.1.2.2 and prior 22.8R2.4 and prior |
| PoC Available | Unknown. None identified as of October 14, 2026. |
| Exploitation Status | Yes. Ivanti confirms exploitation in the wild against a limited number of customers. Listed in the CISA KEV catalog on October 13, 2026. |
| Patch Status | Fixed per Ivanti in versions 25.1.1.2, 25.1.3.0, 25.1.3.1, and 22.8R2.5. |
Affected Assets
Ivanti’s advisory lists three affected ranges: 25.1.1.1 and prior, 25.1.2.2 and prior, and 22.8R2.4 and prior. Versions 22.7R2.14 and prior are not affected, and Ivanti states that 25.1.3.0 and later do not contain the vulnerability. Ivanti also notes that the 22.7 and 22.8 lines reach end of life on January 31, 2027.
Censys currently detects 7,604 Ivanti Connect Secure hosts and 269,319 web properties, excluding honeypot-labeled assets. These are totals for the product, not counts of unpatched or vulnerable systems. The web property count is far larger than the host count because the web index records each hostname and HTTP property served by a detected instance rather than each appliance. The host count is the better measure of distinct appliances.
Censys Query
We currently detect 7,604 hosts and 269,319 web properties with Ivanti Connect Secure, using this query:
(
  host.services.software: (vendor: "ivanti" and product: "connect_secure")
  or web.software: (vendor: "ivanti" and product: "connect_secure")
) and not labels:"HONEYPOT"
The honeypot exclusion removes 29 hosts (0.4%) from the unfiltered host count of 7,604 and about 40,400 web properties (13.0%) from the unfiltered web count of 309,707. Censys detection reads the major and minor version only, so these counts cannot separate vulnerable builds from fixed ones.
PoC Available?
Neither the NVD record nor the CISA KEV entry references public exploit code, and no proof-of-concept from a trusted source has been identified as of October 14, 2026.
Exploitation Status
CISA added CVE-2026-104935 to the KEV catalog on October 13, 2026, with a remediation due date of October 16, 2026. The KEV entry marks known ransomware campaign use as Unknown and flags the vulnerability for CISA’s forensic triage requirements.
Patch Status
Ivanti lists the following patches: 25.1.1.2 (released October 5, 2026) for 25.1.1.1 and prior; 25.1.3.0 (released July 2026) or 25.1.3.1 for 25.1.2.2 and prior; and 22.8R2.5 (released October 12, 2026) for 22.8R2.4 and prior.
Versions 22.7R2.14 and prior are not affected. Ivanti recommends that 22.8.x customers update to 25.1.1.2 or later, using 22.8R2.5 only where that is not immediately possible. Ivanti’s advisory lists no workaround as of October 14, 2026. Volexity reports that the privilege escalation flaw in the same chain was not yet patched as of its October 13, 2026 post and that Ivanti expects to fix it in a future release.
Patching does not remove persistence an attacker has already installed. An appliance that was exposed on an affected version since October 3, 2026 warrants investigation regardless of its current patch state. Volexity’s indicators of compromise are published on GitHub.