CVE-2026-102255 is a critical (CVSS 10.0) pre-authentication server-side request forgery and unintended proxy vulnerability in the Work Place interface of SonicWall SMA1000 series appliances (models 6210, 7210, 8200v). Per SonicWall’s advisory SNWLID-2026-0017, “a remote unauthenticated attacker could potentially exploit this vulnerability to direct the appliance to issue requests on their behalf and reach internal functionality and perform unauthorized operations”.
The same bulletin also discloses three lower-severity, post-authentication vulnerabilities in the SMA1000 Appliance Management Console (AMC):
- CVE-2026-102256 (OS command injection, CVSS 7.8)
- CVE-2026-102257 (Zip Slip path traversal, CVSS 7.2)
- CVE-2026-102258 (stored cross-site scripting, CVSS 5.5)
Each of those three requires an attacker to already hold valid AMC administrator credentials, so CVE-2026-102255 is the one that matters for unauthenticated Internet-facing exposure.
SonicWall states it has no evidence of in-the-wild exploitation of any of the four as of this writing. This is the third pre-authentication SSRF SonicWall has patched in this same Work Place interface in 2026: CVE-2026-15409 (July) and CVE-2026-83548 (September) were both independently confirmed exploited and added to the CISA Known Exploited Vulnerabilities (KEV) catalog shortly after disclosure. Censys currently detects several thousand SonicWall SMA1000/Secure Mobile Access instances across the host and web indexes.
Details
| Field | Description |
| CVE-ID | CVE-2026-102255, CVSS 3.0 10.0 (Critical), vendor-assigned |
| Date of Disclosure | SonicWall advisory SNWLID-2026-0017 first published October 6, 2026; NVD CVE record published October 7, 2026 |
| Affected Assets | SonicWall SMA1000 series appliances (models 6210, 7210, 8200v) running the Work Place interface. SSL-VPN on SonicWall firewall products and the SMA 100 Series product line are explicitly not affected |
| Vulnerable Software Versions | 12.4.3-03526 (platform-hotfix) and earlier12.5.0-02952 (platform-hotfix) and earlier |
| PoC Available | No, as of this writing. |
| Exploitation Status | Not confirmed. Not listed in the CISA Known Exploited Vulnerabilities (KEV) catalog as of October 7, 2026 |
| Patch Status | SonicWall fixed the issue in 12.4.3-03670 (platform-hotfix) and 12.5.0-03082 (platform-hotfix), released alongside the October 6, 2026 advisory |
Affected Assets
SonicWall’s advisory lists the affected product as SMA1000 series appliances, hardware models 6210, 7210, and 8200v, running 12.4.3-03526 (platform-hotfix) and older, or 12.5.0-02952 (platform-hotfix) and older. SonicWall states the vulnerability does not affect SSL-VPN running on SonicWall firewall products, or the SMA 100 Series product line, which is a separate codebase from the SMA1000 series this advisory covers.
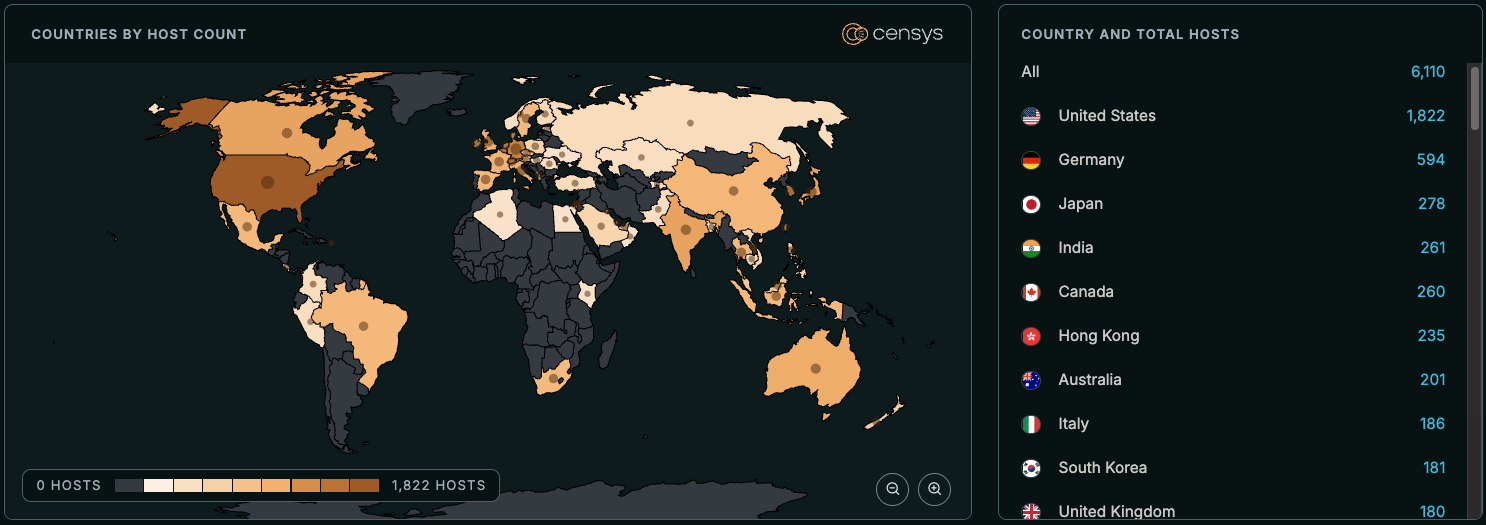
Censys currently detects SonicWall SMA1000/Secure Mobile Access instances across both the host and web indexes. A meaningful share of the raw count in each index is honeypot-labeled: on the host index, 8,367 instances drop to 5,966 after excluding hosts labeled as honeypots, a 28.7% reduction; on the web index, 43,777 drop to 39,310, a 10.2% reduction. The honeypot-excluded figures are reported below.
Censys Query
We currently detect 5,966 hosts and 39,310 web properties running SonicWall SMA1000/Secure Mobile Access, based on the following query:
(host.services.software:(vendor="sonicwall" and product="secure_mobile_access") or web.software:(vendor="sonicwall" and product="secure_mobile_access")) and not labels:"HONEYPOT"
This query identifies product presence only.
PoC Available?
No public proof-of-concept exploit code has been identified for any of these vulnerabilities as of this writing.
Exploitation Status
Not confirmed. None of these vulnerabilities are listed in the CISA KEV catalog as of October 7, 2026, and SonicWall’s advisory states “there is currently no evidence any of the vulnerabilities addressed in this release are being exploited in the wild.”
This is nonetheless the third pre-authentication SSRF SonicWall has disclosed in this same SMA1000 Work Place interface in 2026. CVE-2026-15409, disclosed in July 2026, and CVE-2026-83548, disclosed in September 2026, were each independently confirmed to have been exploited and added to the CISA KEV catalog within days of disclosure.
Patch Status
SonicWall fixed all four vulnerabilities in 12.4.3-03670 (platform-hotfix) and higher, or 12.5.0-03082 (platform-hotfix) and higher, available from mysonicwall.com.
Organizations unable to patch immediately should restrict access to the SMA1000 Appliance Management Console (AMC), to a VPN or an IP allowlist rather than leaving it Internet-facing, since it is not intended to be a public-facing administrative interface. Patching does not remove any access an attacker may already have obtained; any appliance confirmed to have been running an affected build while Internet-reachable warrants a compromise assessment independent of its current patch state.