Vulnerability Description
CVE-2026-104286 is a critical path traversal vulnerability in Fortinet FortiMail (CVSS 3.1 9.8) that may allow a remote, unauthenticated attacker to write arbitrary files to the appliance’s underlying system with crafted HTTP or HTTPS requests. Fortinet states that it has been reported to be exploited in the wild, with CISA adding it to their Known Exploited Vulnerabilities (KEV) catalog on October 1, 2026
Fortinet provides three workarounds:
- Disable the IBE (Identity-Based Encryption) feature.
- Disable access to the FortiMail webmail interface from the internet, or limit it to trusted private networks.
- Where a web application firewall sits in front of the appliance, block POST requests to
/ibethat contain../.
Impact
Fortinet’s published indicators include a cron entry referencing /migadmin, an archive account with a remote destination, and encryption log entries showing IBE decryption errors or failed internal user logins. Review any FortiMail appliance that ran an affected version to check for their presence using Fortinet’s indicators in FG-IR-26-175.
Details
| Field | Description |
| CVE-ID | CVE-2026-104286, CVSS 3.1 9.8 (Critical), assigned by Fortinet |
| Date of Disclosure | Fortinet: October 1, 2026. |
| Affected Assets | Fortinet FortiMail on the 7.2, 7.4, 7.6 and 8.0 branches. 7.0 is not in Fortinet’s advisory table, though Fortinet’s CVE record lists 7.0.0 through 7.0.9 |
| Vulnerable Software Versions | 8.0.0 through 8.0.1; 7.6.0 through 7.6.6; 7.4.0 through 7.4.8; 7.2.0 through 7.2.9 |
| PoC Available | No public proof-of-concept as of October 2, 2026 |
| Exploitation Status | Reported exploited in the wild by Fortinet, with no threat actor attributed as of October 2, 2026. Added to the CISA Known Exploited Vulnerabilities (KEV) catalog October 1, 2026, with a federal remediation due date of October 4, 2026 |
| Patch Status | No fixed builds released as of October 2, 2026. Fortinet lists 8.0.2, 7.6.7 and 7.4.9 as upcoming; 7.2 users must move to 7.4 or later |
Censys ARC Perspective
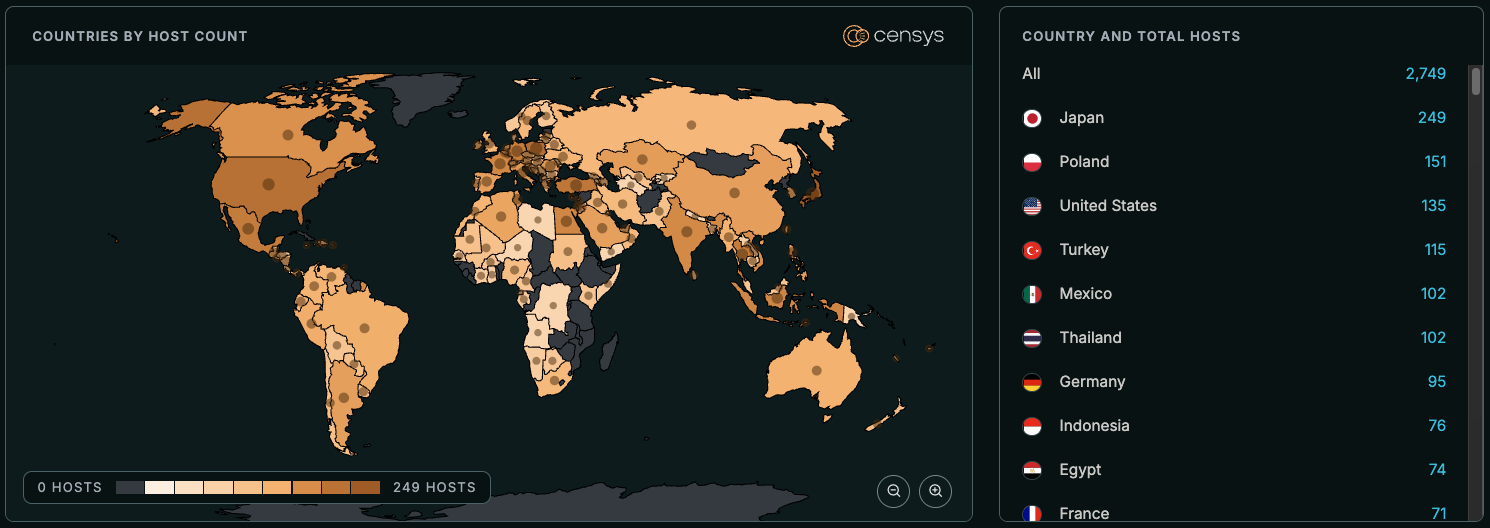
Censys Platform shows roughly 2,800 FortiMail hosts on the internet, after excluding honeypots, which make up more than a third of the hosts presenting as FortiMail. Japan and Poland have the most, but no single country accounts for more than 10 percent of them.
About 350 of those hosts, roughly an eighth, show FortiMail on an HTTPS port. The Censys Rapid Response team notified customers of potentially vulnerable instances in their attack surfaces.
Censys Queries
host.services.software:(vendor="fortinet" and product="fortimail") and not labels:"honeypot"
host.services.software: (vendor: "Fortinet" and product: "FortiMail") or web_entity.instances.software: (vendor: "Fortinet" and product: "FortiMail")